Cybersecurity Companies in Qatar: 6 Firms Compared for 2026
Founder and Principal Security Consultant - CISSP, CEH, CHFI, Mandiant

We have probably seen your problem before. Our smallest client had eight employees. Our largest secures the nuclear power plant of the United Arab Emirates. Whatever shape yours is, tell us about it and we will tell you how we would fix it.
Qatar has its own national information assurance framework and its own data protection law, and between them they drive most serious security spending in the country. Knowing which applies to you matters more than knowing which vendor is fashionable. This guide compares six companies with a real Doha presence on what they charge, how big they are, and what they actually do.
Disclosure: this guide is published by Atlant Security, which appears at number 4 of 6 below. We are not a reseller or partner of any firm listed, none paid for placement, and none saw this before publication. Every company here was checked against its own live website on 14 September 2026. Strengths and weaknesses are our editorial judgement; each quoted line is taken verbatim from the firm’s own site.
What changed in this edition: This edition was rebuilt. The previous version listed only service categories, lettered A through G, and named no companies at all, which is not a comparison and cannot help anyone choose a supplier. Every firm below now has a verified Qatari presence and a screenshot of its site as it looked in September 2026. One candidate was dropped during fact-checking because it turned out to be an Arabic AI and software development company rather than a security firm, and one entry’s domain has moved, which we note in its listing.
Start Here: the 30 Second Version
If you read nothing else on this page, read the row that describes you. Every provider is compared in detail further down, but choosing the right category of firm matters far more than choosing between two firms in the same category.
| If this is you | Buy this first | Because |
|---|---|---|
| A government entity or critical sector organisation | A NIA risk classification and gap assessment | Classification comes first. It decides how much of the standard actually applies to you. |
| A supplier bidding for Qatari government work | A gap assessment against the standard the tender names | The contract condition sets your baseline, whatever your own risk appetite says. |
| You need an actual break-in attempt | Offensive testing from the specialist below | Only one firm in this group does this, which is typical of the Qatari market. |
| You are managing compliance as an ongoing programme | A GRC platform, plus somebody to do the work | A platform is not a service. Somebody still has to implement the controls. |
| You do not know which of these you are | A scoped, fixed-price audit | The cheapest thing to buy first is the ordering. |
Atlant Security editorial assessment, September 2026. This is our reading of the market, not a figure taken from any published source.
Does a Qatar Cybersecurity Company Need to Be in Qatar?
For government and semi-government work, yes, frequently as a precondition. Qatari public sector procurement favours locally established providers, and requirements around data residency and local delivery are real rather than nominal. If your work touches that sector, ask about eligibility before capability.
For commercial work, the usual rules apply: judge on specialism and on who is actually assigned. Doha is compact, so a local provider can be on site quickly, which removes much of the argument for preferring a remote specialist.
The specific local advantage worth paying for is familiarity with Qatar’s own frameworks. A provider who has taken clients through an assessment against the national information assurance standard knows how it is applied in practice, which is not the same as having read the document.
Which Qatari Framework Applies to You?
Qatar has a national information assurance framework that sets out control requirements and a classification approach for information assets, and it is the reference point for government entities and for organisations designated as critical. Unlike a risk-based standard it tells you what to implement, which makes gap assessment the natural first engagement. We cover what it requires on our Qatar NIA compliance page.
Separately, Qatar has a personal data protection law applying to organisations handling personal data, with obligations around consent, purpose and security. It was among the earlier comprehensive data protection regimes in the Gulf. As always, confirm the operative detail against the regulator’s current guidance rather than a vendor summary, this one included.
Financial institutions face additional supervisory expectations from their own regulator, and organisations in energy carry requirements flowing from operator contracts rather than from statute. That pattern, obligations arriving through contracts rather than law, is common across the Gulf and catches suppliers who assume their size exempts them.
Operationally, Qatar’s exposure looks like the rest of the Gulf. Business email compromise against invoiced cross-border payments is the most common expensive incident, because the economy runs on international contracting. Large infrastructure and energy projects also concentrate operational technology that cannot be assessed with ordinary IT tooling and needs a provider who understands the difference.
Work out which one you are
Which rulebook binds you in Qatar?
Qatar runs a national information assurance regime with a formal certification attached, and it reaches suppliers to government as well as government itself.
A government entity or a critical sector organisation
The National Information Assurance standard, operating inside the National Information Security Compliance Framework
Enforced by the National Cyber Security Agency (NCSA)
A vendor or supplier to one of those entities
The same standard, arriving through your contract rather than directly
Enforced by your client, and the NCSA behind them
You hold personal data in Qatar
Qatar personal data protection law
Enforced by the national data protection authority
The three most common situations. The full table below adds a fourth and gives the sourcing for each row.
| Your situation | What applies | Who enforces it | What it changes when you buy |
|---|---|---|---|
| A government entity or a critical sector organisation | The National Information Assurance standard, operating inside the National Information Security Compliance Framework | The National Cyber Security Agency (NCSA) | NIA certification is the formal evidence of compliance. See Qatar NIA compliance. |
| A vendor or supplier to one of those entities | The same standard, arriving through your contract rather than directly | Your client, and the NCSA behind them | Government contracts increasingly require proof of NIA alignment as a condition of doing business. |
| You hold personal data in Qatar | Qatar personal data protection law | The national data protection authority | One firm below sells a compliance platform built specifically around Qatar frameworks. |
| You are the Gulf arm of a foreign parent | Local law, plus group standards and any GDPR flowing down by contract | Your head office, your auditors and your customers | Usually both apply. Scope it explicitly rather than assuming. |
Framework names and scope are as published on Atlant Security’s own Qatar NIA page, which carries the detail. Confirm your own position with counsel. This is not legal advice.
Cybersecurity Companies in Qatar: Side-by-Side Comparison
All 6 firms below have a real presence in the Qatar area. The table is sorted in the same order as the reviews that follow.
| Provider | Based | Team size | Hourly rate | Best for |
|---|---|---|---|---|
| malomatia | Doha, Qatar | 500+ | Not published | Qatari government entities and large organisations needing a national-scale provider |
| TrekShield | Doha, Qatar | 50-249 | $50-$99 | Qatari organisations that need an actual break-in attempt, not a scan |
| QRTD Information Technology | Doha, Qatar | 10-49 | Not published | Qatari organisations buying a structured security programme rather than a project |
| Atlant Security | Remote, serving 14 countries | Small senior team | Fixed price, not hourly | Companies that need someone to decide what to do and then implement it |
| Vantage GRC | Doha, Qatar | 2-9 | $50-$99 | Qatari organisations managing NIA or data protection compliance as an ongoing programme |
| Secyour | Doha, Qatar | 2-9 | Not published | Smaller Qatari organisations wanting continuous scanning at low cost |
Team size, hourly rate and minimum engagement are as published by each firm on the Clutch directory, checked 14 September 2026. They are the firms’ own figures, not our measurements. “Best for” is Atlant Security’s editorial assessment.
What kind of firm each one actually is
The table above compares them on price and location. This one compares them on what they are, which is the comparison that decides whether the engagement works. Most bad purchases in this market are the right firm in the wrong category.
| Provider | What kind of firm it is | What the engagement ends with | The limitation this guide flags |
|---|---|---|---|
| malomatia | Full-service national provider | An enterprise relationship across several towers | Government and large enterprise oriented; SMEs are not the target |
| TrekShield | Offensive testing | A report describing how they got in | Testing only; nobody will remediate the findings for you |
| QRTD Information Technology | Consultancy | A prioritised plan, and with some firms the fixes as well | $50,000 minimum excludes smaller or exploratory work |
| Atlant Security | Consultancy | A prioritised plan, and with some firms the fixes as well | No help desk, so day-to-day IT support still needs a local provider |
| Vantage GRC | Product vendor | A platform your team runs, or its managed tier | A platform, not a service; somebody still has to do the underlying work |
| Secyour | Product vendor | A platform your team runs, or its managed tier | Automated scanning is not a penetration test and should not replace one |
Category is our reading of each firm’s own published description, quoted in its entry below. The limitation column is taken verbatim from the same entry. Checked against each firm’s live site in September 2026.
Read the Atlant Security row the same way you read the others. We are a consultancy. There is no help desk, no monitoring platform and nothing to resell, and that is a limitation as much as a position. If what you need is somebody to answer the phone when a laptop dies, buy from one of the managed providers on this page instead. We are here because deciding what to fix and in what order is a separate purchase from keeping the estate running.
The 6 Best Cybersecurity Companies in Qatar for 2026
Ordered by fit for a Qatari buyer. The first is the national-scale provider, then an offensive testing specialist, then programme and platform options.
1. malomatia
Doha, Qatar · Website: malomatia.com
Best for: Qatari government entities and large organisations needing a national-scale provider
malomatia is a long-established Qatari technology services company with deep roots in the public sector, and it occupies the position in Qatar that national champions occupy elsewhere in the Gulf. For a government entity or a large Qatari organisation, a provider with local establishment, local delivery and existing public sector relationships is frequently a precondition rather than a preference. It is an enterprise relationship with the procurement timeline that implies.
Strengths
- Deep Qatari public sector experience and local delivery
- National scale, with continuity a small consultancy cannot offer
Watch out for
- Government and large enterprise oriented; SMEs are not the target
- No published pricing and formal, lengthy procurement
Team size: 500+ · Rate: Not published · Minimum engagement: Enterprise engagement
2. TrekShield
Doha, Qatar · Website: trekshield.com
Best for: Qatari organisations that need an actual break-in attempt, not a scan
TrekShield is the offensive security specialist in this group, which makes it unusual in the Qatari market where most providers are managed services or integration businesses. The distinction matters commercially: a vulnerability scan and a penetration test are routinely sold under the same word, and only one of them produces a narrative of how somebody would actually get in. If a regulator, customer or insurer has asked you for a penetration test, this is the category you need.
TrekShield - Professional Penetration Testing Services
How TrekShield describes itself on trekshield.com, September 2026
Strengths
- Genuine offensive testing specialism, uncommon among Qatari providers
- Published rate band with a clear $10,000 engagement floor
Watch out for
- Testing only; nobody will remediate the findings for you
- $10,000 minimum rules out very small scopes
Team size: 50-249 · Rate: $50-$99 · Minimum engagement: $10,000+
3. QRTD Information Technology
Doha, Qatar · Website: qrtd.qa
Best for: Qatari organisations buying a structured security programme rather than a project
QRTD names cybersecurity first in its own positioning and takes engagements from $50,000, which is the highest floor in this group and tells you plainly what it does: multi-month programmes rather than bounded projects. That shape fits an organisation building a compliance programme from a standing start against Qatar’s national frameworks, and does not fit a company that simply wants a test.
QRTD | Cyber Security and IT Solution Provider in Qatar
How QRTD Information Technology describes itself on qrtd.qa, September 2026
Strengths
- Security-first positioning with a Doha base
- Structured for substantial multi-month programmes
Watch out for
- $50,000 minimum excludes smaller or exploratory work
- No published hourly rate
Team size: 10-49 · Rate: Not published · Minimum engagement: $50,000+
4. Atlant Security
Remote, serving 14 countries · Website: atlantsecurity.com
Best for: Companies that need someone to decide what to do and then implement it
Atlant Security is a consultancy rather than a managed services provider or a product vendor, and the distinction is the reason it is on this list at all. There is no help desk, no monitoring platform and nothing to resell. What it does is the part most local providers leave to you: an audit that produces a prioritised remediation plan with named owners and effort estimates, and the same engineers then implementing the fixes. The firm has run 200+ security assessments across 14 countries since 2013, works to fixed prices rather than hourly billing, and is vendor-independent, so the recommendation carries no resale commission. For a company that does not yet know whether it needs an MSP, a penetration test or a compliance programme, that ordering is the useful thing to buy first.
Strengths
- Fixed price, so scope and invoice are agreed before work starts
- Implements the fixes rather than stopping at a findings report
- Vendor-independent, with no product resale margin behind the advice
Watch out for
- No help desk, so day-to-day IT support still needs a local provider
- No 24/7 monitoring platform of its own; continuous detection goes to a partner
- Remote-first, so regular on-site presence is not the model
Team size: Small senior team · Rate: Fixed price, not hourly · Minimum engagement: $8,000+
5. Vantage GRC
Doha, Qatar · Website: vantage.com.qa
Best for: Qatari organisations managing NIA or data protection compliance as an ongoing programme
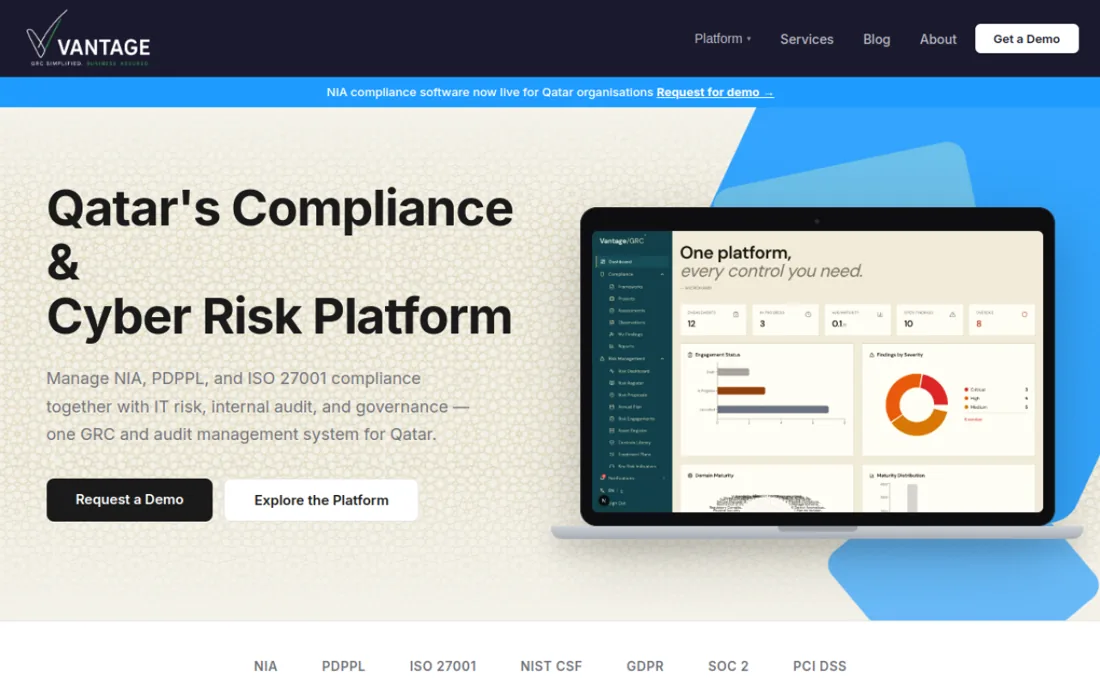
Vantage is a governance, risk and compliance platform built specifically around Qatar’s own frameworks, naming the national information assurance standard and the country’s personal data protection law directly in its positioning. That specificity is the point. Generic GRC tooling forces you to map a foreign control library onto local requirements, while a platform built for the local frameworks starts where you actually are. It manages compliance rather than performing it.
GRC Software Qatar
How Vantage GRC describes itself on vantage.com.qa, September 2026
Strengths
- Built around Qatar’s own national frameworks rather than mapped onto them
- Turns compliance from a periodic scramble into a maintained state
Watch out for
- A platform, not a service; somebody still has to do the underlying work
- Very small team behind it
Team size: 2-9 · Rate: $50-$99 · Minimum engagement: $10,000+
6. Secyour
Doha, Qatar · Website: secyour.pro
Best for: Smaller Qatari organisations wanting continuous scanning at low cost
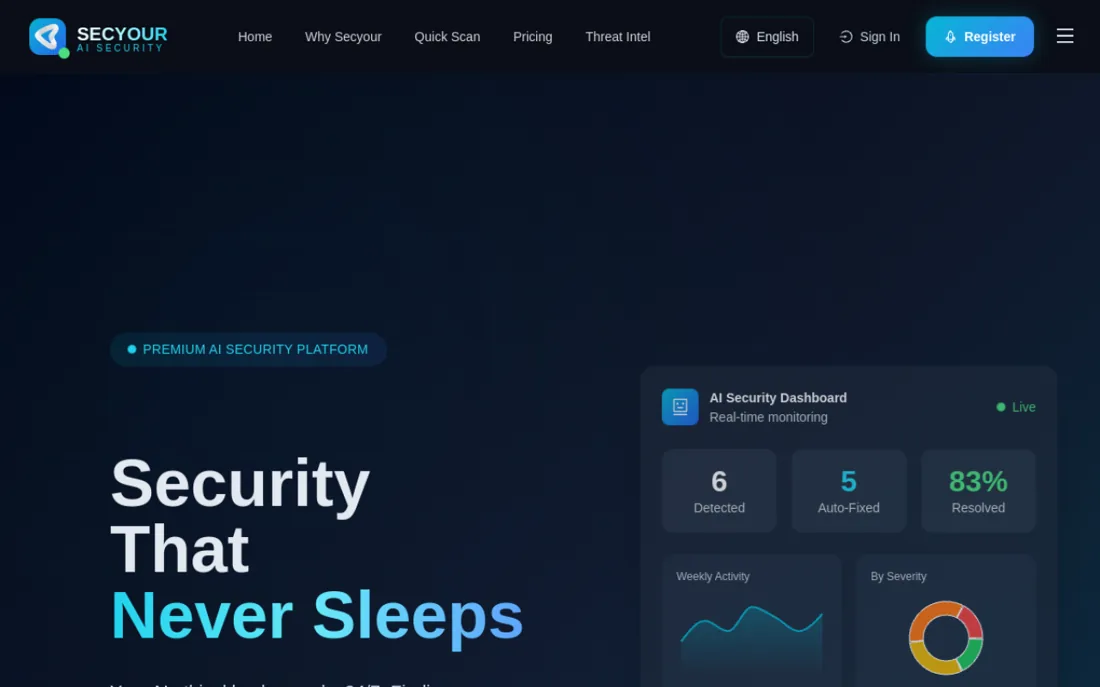
Secyour is a small Doha operation offering a security scanning platform. Be clear about what that is and is not: automated scanning finds known, catalogued weaknesses continuously and cheaply, which is genuinely useful as a baseline hygiene measure. It does not find the business logic flaws and chained weaknesses a human tester finds, and it should not be purchased as a substitute for one. Note the domain moved from secyour.org to secyour.pro.
Secyour Scanner - Security Scanning Platform
How Secyour describes itself on secyour.pro, September 2026
Strengths
- Low-cost continuous scanning as a baseline hygiene layer
- Locally based, so support sits in your time zone
Watch out for
- Automated scanning is not a penetration test and should not replace one
- Very small team; neither rate nor minimum is published
Team size: 2-9 · Rate: Not published · Minimum engagement: Not published
How to Choose a Cybersecurity Company in Qatar
The providers below fall into several quite different categories, which makes the selection process matter more than the shortlist. Work through these five steps in order.
- Work out which of the things below you are buying
A managed provider keeps your estate running day to day. A testing firm tries to break in and reports how it went. A consultancy decides what you should do and in what order. A product vendor sells you a platform somebody then has to operate. The table above says which is which.
- Ask who fixes the problem after it is found
A scan, an audit and a penetration test all end with a document. Somebody then has to change firewall rules, rebuild permissions, roll out multi-factor authentication and argue with a vendor about a legacy application. Ask in writing whether remediation is included, excluded, or billed separately.
If the gap between annual tests is what worries you, Pentestas closes it. Same coverage across web apps, APIs, cloud and internal network, evidence you can hand a developer, and a turnaround measured in days.
- Get the scope and the price in writing before anyone starts
A proposal that prices security services without listing what is monitored, tested or documented is not a proposal you can hold anyone to. Ask for a fixed or capped price and an explicit list of exclusions. The price transparency panel further down shows how many of these firms publish anything at all.
- Get your risk classification settled before anything is scoped
Under the Qatari regime the classification of your systems drives how much of the standard applies. Scoping an engagement before that is settled means either paying for controls you do not need or discovering halfway through that the scope was wrong. It is the cheapest step in the programme and the one most often skipped.
- Ask what you keep if you leave after twelve months
Documentation, configurations, log history, tenancy ownership. If the answer is that you keep nothing, you are not buying a security programme, you are renting one, and the renewal conversation will reflect that.
Good signs
- They name the engineer who will do the work, and you can check that person exists
- They tell you what is out of scope before you ask
- They are willing to quote a fixed price for a bounded piece of work
- They ask about your customers and your parent company, not just your firewall
- They can say plainly which parts of the job they would subcontract
Walk away if
- Security is one of a dozen services listed and nobody on the team does it full time
- The proposal prices security services as a single line with no itemised scope
- The recommendation happens to be the product they resell
- They will not put the remediation position in writing
- They quote a NIA programme before classifying your systems
Five questions worth putting in the RFP
| Ask this | Why it matters | What a good answer sounds like |
|---|---|---|
| What proportion of your revenue is security work? | A directory search returns many firms listing cybersecurity among a dozen services. | A number, followed by the names of the people who do it full time. |
| Who specifically will be assigned, and what is their background? | Small teams sell with a senior and deliver with a junior. It is the most common complaint. | A name, a history you can verify, and a willingness to put it in the contract. |
| What does your managed security tier actually monitor, and during which hours? | MSSP is a marketing term as often as it is an operating model. | Named data sources, named hours, and who reads an alert at 03:00. |
| Is remediation included, excluded, or billed separately? | This is where the budget you did not plan for appears. | One of the three words, in writing, before you sign. |
| What happens contractually if we are breached during the engagement? | It reveals how much of the risk the provider is genuinely taking on. | A clear, unembarrassed answer. Whether they have thought about it matters most. |
Atlant Security editorial, September 2026. These are the questions we would ask, based on what goes wrong in engagements we are called in to rescue.
What Cybersecurity Costs in Qatar
Qatari pricing splits like the rest of the Gulf. The national-scale provider does not publish rates and runs formal procurement. The commercial firms publish bands around $50 to $99 per hour with minimum engagements from $10,000 to $50,000, which is a higher floor than Dubai and reflects a market weighted toward larger projects.
That higher floor is worth planning around. A small Qatari business looking for a bounded first engagement has fewer options here than it would in the UAE, and may find that an independent remote assessment is the most practical way to establish what it needs before committing to a local programme.
Where a national framework drives the work, budget for evidence and documentation to exceed technical remediation. A fixed-price independent audit generally runs $8,000 to $35,000 and, in a market where obligations arrive from several directions at once, establishing which actually bind you is often the most valuable output.
The practical problem with buying here
Price transparency among these providers
What each firm publishes about what it charges, before you have spoken to anyone.
| Provider | Hourly rate published | Minimum engagement published | Fixed price offered |
|---|---|---|---|
| malomatia | |||
| TrekShield | |||
| QRTD Information Technology | |||
| Atlant Security | |||
| Vantage GRC | |||
| Secyour |
2 of the 6 publish an hourly rate. 4 publish a minimum engagement. Expect to ask, and expect to get the answer in writing before anyone starts.
Rates and minimums as published by each firm on the Clutch directory, checked 14 September 2026. A cross means the figure is not published. It is not a finding that the firm refuses to quote.
| What you are buying | Price | Where this number comes from |
|---|---|---|
| Hourly rate, published bands | $50-$99 | Published by 2 of the 6 firms above on the Clutch directory. |
| Minimum engagement, published | $8,000+ to $50,000+ | Published by 4 of the 6 firms above. |
| Fixed-price independent security audit | US$8,000 to US$35,000 | Atlant Security estimate, based on our own engagements. Not a published figure. |
| Penetration test, bounded scope | US$8,000 to US$20,000 | Atlant Security estimate. Varies more with scope than with provider. |
| Managed detection and response, per year | From US$30,000 | Atlant Security estimate. The variable is who reads the alerts, not the platform licence. |
| Gap assessment against Qatar NIA compliance | Quoted per organisation | Scope depends on which framework applies. See our Qatar NIA compliance page. |
Rows marked as published are the firms’ own figures, checked 14 September 2026. Rows marked as an estimate are Atlant Security’s, are labelled as such, and should be treated as a planning range rather than a quotation.
Frequently Asked Questions: Cybersecurity Companies in Qatar
Which cybersecurity companies are actually based in Qatar?
malomatia is a long-established Qatari technology services company with deep public sector roots. TrekShield, QRTD Information Technology, Vantage GRC and Secyour are all Doha based. Atlant Security works remotely with clients across 14 countries.
What is the Qatar NIA framework and does it apply to us?
It is Qatar’s national information assurance framework, setting out control requirements and an information classification approach. It is the reference point for government entities and organisations designated as critical. Because it is prescriptive rather than risk-based, a gap assessment against it is usually the sensible first engagement.
Who should we use for penetration testing in Qatar?
TrekShield is the dedicated penetration testing firm in this group. Be clear about what you are buying: a penetration test is a human attempt to break in, which is a different and more useful service than an automated vulnerability scan, even though both are frequently sold using the same word.
What does a cybersecurity company cost in Qatar?
Commercial firms publish bands around $50 to $99 per hour, with minimum engagements from $10,000 to $50,000. The national-scale provider does not publish pricing. A fixed-price independent audit generally runs $8,000 to $35,000 depending on scope.
We are a small Doha business. Are these firms all too big for us?
The minimum engagements here are higher than in Dubai, so possibly. The smaller platform and scanning options on this page are more accessible, and an independent remote assessment is often the most practical way to work out what you actually need before committing to a local programme with a five-figure floor.
Does the Qatari NIA standard apply to private companies?
Directly, it applies to government entities and organisations in Qatar’s critical sectors. In practice it extends to their vendors and suppliers, because government contracts increasingly require proof of NIA alignment as a condition of doing business. A private company with no public sector exposure is usually outside it.
What is NIA certification?
It is the formal recognition that an organisation has met the requirements of the National Information Assurance framework, following an assessment of your controls against the standard. It is the evidence government entities and critical sector organisations use to demonstrate compliance. Our Qatar NIA page explains how the classification and assessment steps run.
Not sure which of these you actually need?
That is the question a fixed-price security audit answers. We assess what you have, tell you what to fix and in what order, and give you a plan you can hand to any provider on this page, including one of our competitors. 200+ assessments across 14 countries since 2013, fixed price agreed before we start.
See what a fixed-price audit coversRelated reading: the 15 largest computer security companies compared, our fixed-price IT security audit, and virtual CISO services.
This comparison is deliberately short. For the long version, the cybersecurity company directory filters by category, location and credentials.

Alexander Sverdlov
Founder of Atlant Security. CISSP, CEH, CHFI and Mandiant certified. Author of 2 information security books, cybersecurity speaker at the largest cybersecurity conferences in Asia and a United Nations conference panelist. Former Microsoft security consulting team member, external cybersecurity consultant at the Emirates Nuclear Energy Corporation.
Connect on LinkedIn