Compliance & Framework Readiness
Walk Into the Certification Audit Already Audited.
The clause 9.2 internal audit your certification body expects, performed by an auditor who did not build or operate your ISMS. Also covers ISO 42001 AI management systems.
$4,500 per audit. $7,900 for the annual programme. Fixed.
Clause 9.2 requires objectivity, which rules out auditing a system you run yourself.
SEE THE DELIVERABLE
See what a useful
audit report looks like.
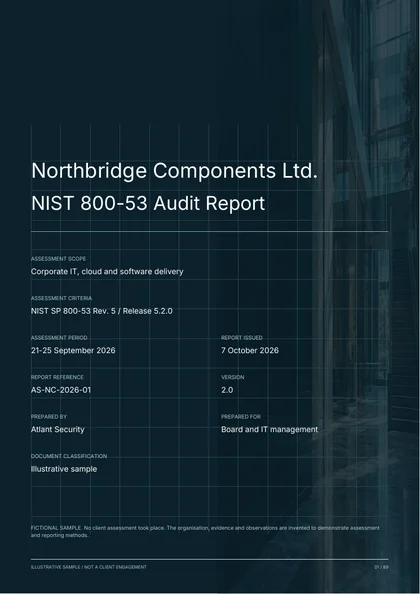
Review 120 assessment tests across all 20 NIST SP 800-53 control families, including AWS, Microsoft 365, secure software development and DevSecOps. Includes technical findings and a 12-month remediation plan.
89 pages. 20 control families. 32 findings. 13 graphs and diagrams.
Illustrative NIST SP 800-53 assessment. The organisation, evidence and findings are fictional.
Get the sample report
A free PDF. Enter your email and company name, and we’ll email you a download link.
Runs the internal audit himself, so the findings still hold up at the certification audit.
Connect on LinkedIn01 / THE DETAIL
Why the Internal Audit Keeps Failing
Clause 9.2 requires an internal audit that is objective and impartial, which rules out auditing a system you built or run. Most failures we are called in to fix are not technical at all, they are the same person on both sides of the control.
Your certification body visit is booked and clause 9.2 is not evidenced
ISO 27001 requires internal audits at planned intervals, by auditors who are objective and impartial about what they audit. A missing or self-performed internal audit is the first nonconformity an external auditor looks for, because it is the easiest to find.
The only person who could audit the ISMS is the person who runs it
In a team of five to fifty, the ISMS manager cannot audit their own work and nobody else has the standard in their head. The result is either no audit or an audit that does not survive a certification body question.
The consultant who built your ISMS offered to audit it too
That is the same independence problem with a vendor logo on it. Auditing your own implementation is a segregation-of-duties failure. We only audit management systems we did not design or operate, and we say so in the report.
02 / THE DETAIL
What the Audit Covers
A full internal audit covers the management system clauses and the controls you declared applicable. We sample controls in the systems where they live, because a certification body will, and a document-only internal audit gives you false comfort.
03 / THE DETAIL
Independence Is the Product
Clause 9.2 requires auditors to ensure objectivity and impartiality. Many consultancies implement an ISMS and then run its internal audit, mock audit and risk assessment with the same people. Certification bodies notice, and so do customers doing due diligence.
We hold a simple rule: we do not audit management systems we designed or operate, and we do not take the ISMS manager seat for a client we audit. Each report carries a signed independence statement saying so.
If you want us to build your ISMS as well, we will point you to a separate auditor. Turning that work down is what makes the audit worth paying for.
04 / THE DETAIL
Who Uses an External Internal Auditor?
05 / THE DETAIL
Compared With the Alternatives
| Atlant Security | Typical arrangement | |
|---|---|---|
| Independence | We never audit an ISMS we built or operate, and the report states it | The implementation consultant audits their own work |
| Who audits | A CISSP with 200+ assessments across 14 countries, personally | A junior with a checklist template |
| Technical depth | Controls sampled in the live systems: Entra, AWS, endpoints, code | Document review only |
| Shape | An annual programme with a tracker, not a one-off PDF | A single audit, then silence until next year |
| Pricing | Published per audit and per programme | Quoted after the scoping call |
06 / THE DETAIL
How an Audit Cycle Runs
Plan
Audit programme, scope, criteria and schedule agreed with management and aligned to your surveillance or recertification date. Auditor independence confirmed in writing.
Fieldwork
Remote evidence review, interviews with control owners, and sampling of technical controls in the systems themselves rather than in screenshots.
Report
Findings graded as major, minor or opportunity, each with the clause or control reference, root cause and a proposed corrective action.
Follow-up
Nonconformity closure verified before the certification body arrives, and a management review input pack with trends across cycles.
07 / PRICING
Pricing
Published and fixed. An internal audit is two to five auditor days of judgement, and the price reflects that rather than a template with your logo.
Single Internal Audit
One full-scope audit of a single-site ISMS ahead of a surveillance or recertification visit.
- Audit plan and independence statement
- Clauses 4 to 10 and Statement of Applicability
- Control sampling in live systems
- Graded findings report with references
- Nonconformity and corrective action tracker
Annual Audit Programme
Two audits a year, the tracker maintained between them, and management review inputs.
- Everything in the single audit, twice a year
- Audit programme aligned to your CB calendar
- Corrective action follow-up and closure verification
- Management review input pack with trends
- Certification body liaison on audit day
- ISO 42001 integration available
Multi-site and integrated ISO 27001 and ISO 42001 programmes are priced per site in writing before we start. You review the report before you pay.
08 / THE DETAIL
Walk Into the Certification Audit Already Audited
One planning call, an audit programme aligned to your certification body dates, and findings you can close before anyone else sees them.
Book Your Planning Call09 / THE DETAIL
Get Your Audit Plan
Choose a time for your scoping call.
10 / FAQ
ISO 27001 Internal Audit FAQ
What does ISO 27001 actually require for internal audits?
Can we do the internal audit ourselves?
Why will you not audit an ISMS you helped build?
How often do we need one?
Do you also audit ISO 42001?
What do we receive?
How much does it cost?
Is it done remotely?
11 / THE DETAIL