ALL PACKAGES
Executive summary
An independent view of the material risks found in the agreed scope, written for the people accountable for the business.
CYBERSECURITY AUDIT SERVICES
Find the security gaps that matter—and get a practical plan to fix them.
An independent review of your IT environment and security controls, led by Alexander Sverdlov, with scope and price agreed before work begins.
From $5,000
USD · Essentials package · Final price depends on scope.
Review the report before payment under the agreed terms.
200+ assessments across 14 countries.
For business risk, board oversight or an independent review.
01 / DELIVERABLES
Our cybersecurity audit services turn the agreed control review into decisions your management and IT teams can act on. Every package includes an executive summary and remediation priorities. The broader packages add detailed technical reporting, a programme plan and framework mapping.
ALL PACKAGES
An independent view of the material risks found in the agreed scope, written for the people accountable for the business.
ALL PACKAGES
The gaps that need attention, why they matter and the practical actions to address them. The scope sets the depth of supporting evidence.
COMPREHENSIVE & ENTERPRISE
Documented observations, evidence, affected controls and specific remediation instructions for the people implementing the changes.
COMPREHENSIVE & ENTERPRISE
A prioritised, 12-month improvement roadmap with proposed ownership, sequencing and effort estimates.
AGREED FRAMEWORKS
A record of assessed controls and gaps against the framework or frameworks named in your proposal. Coverage follows the package and scope.
Findings reviews and consulting sessions explain the documents; they are not counted as extra reports. Your proposal lists the exact deliverables.
02 / YOUR AUDITOR & CLIENT EXPERIENCE
Former Microsoft Security Consulting team member. CISSP, CEH, CHFI and Mandiant certified, with experience securing nuclear energy infrastructure at ENEC.
Alexander has led more than 200 security assessments across 14 countries. He leads the scope discussion, reviews the controls and explains the findings to your team.
When choosing an IT security audit company, ask who will do the work, which evidence they will review and what your team will receive. At Atlant Security, those answers are part of the proposal.
Meet Atlant Security · Client success stories · Alexander’s background
Watch: how to get your team behind the changes, so the fixes actually land
“Alexander is professional, reliable and available. He is clearly an expert in his field. Building trust in cybersecurity is obviously essential and Alexander has constantly demonstrated that my trust is well-placed.”
“The assessment was really imposing and remarkable. It was beyond my expectations, very detailed, and things were very closely inspected and discussed. It was a great experience working with you.”
03 / REVIEW A SAMPLE
Open a six-page excerpt with an executive summary, scope, control-family results and a detailed finding with corrective actions. No form is required for the excerpt.
Illustrative sample. Northbridge Components Ltd., its systems, evidence and findings are fictional. The example shows reporting depth; it does not define the scope of the $5,000 package.
Open the illustrative excerpt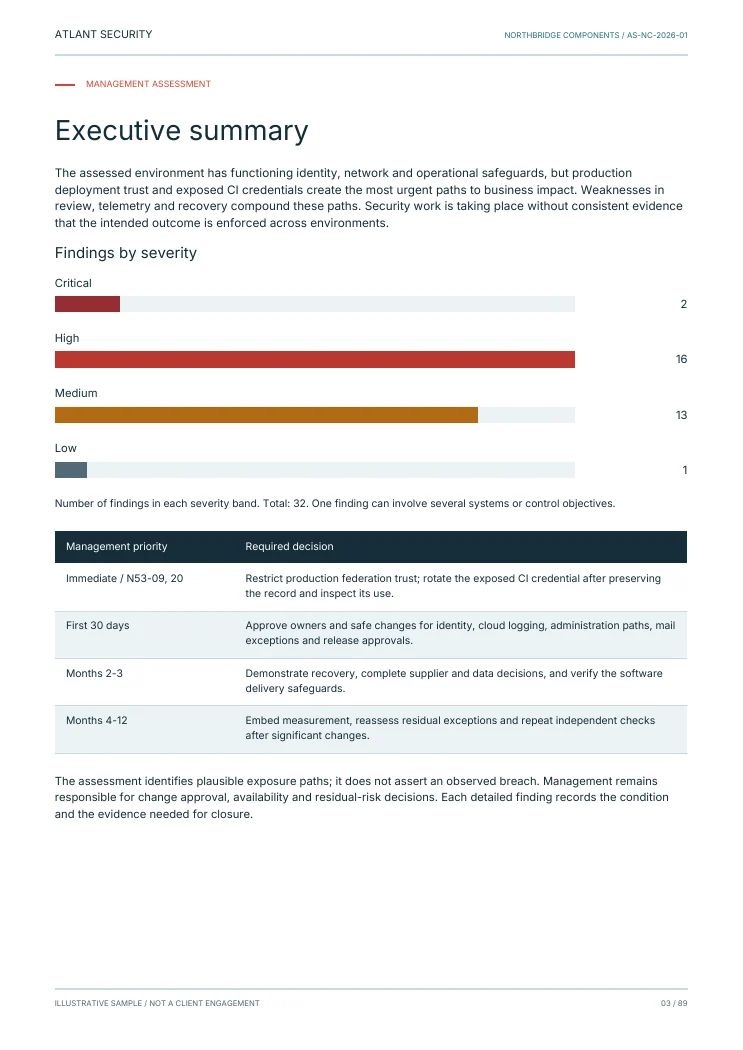
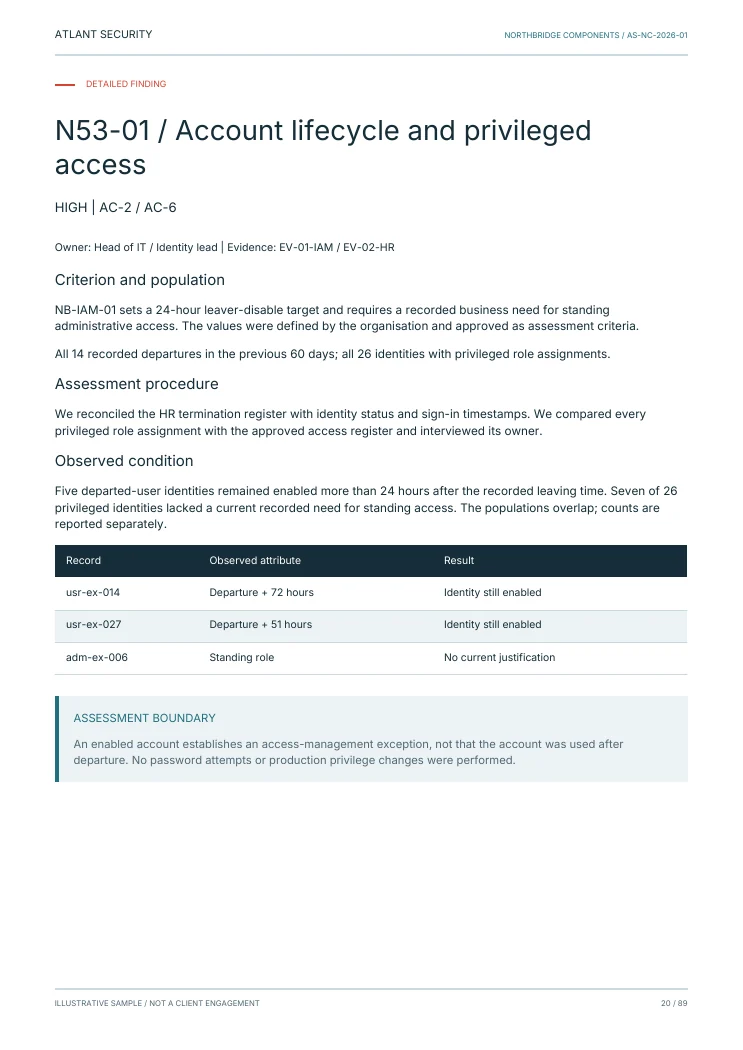
The full example contains 89 pages, selected tests across 20 NIST SP 800-53 control families, technical findings and a 12-month plan. Request it by email using the adjacent form.
A free PDF. Enter your email and company name, and we’ll email you a download link.
04 / SCOPE
We agree the systems, assessment criteria, sampling, access and reporting requirements before the audit starts. Your scope can cover these areas; the package determines how broadly and deeply we assess them.
Account lifecycle, authentication, administrative access, privileges and access to sensitive information.
Endpoints, networks, server configuration and the cloud environments included in the engagement.
Logging, monitoring, incident procedures, backup controls and the evidence behind recovery claims.
Ownership, policies, risk decisions, supplier dependencies and how controls operate day to day.
Secure development, secrets, dependencies and DevSecOps controls in the broader packages where applicable.
Assessment against the agreed criteria. Essentials covers one framework; larger packages can map to several.
NIST SP 800-53 can structure the assessment across its 20 control families. Applicable controls and test depth are selected for your environment. Cloud and software delivery are environments and workstreams within that review, not additional NIST control families.
This is an independent assessment, not a certification engagement. A dedicated Microsoft 365 audit or penetration test can be scoped separately when that is the actual requirement.
05 / SCOPE & PRICING
Three starting points. One written scope and fixed price before work begins. All prices are in USD and subject to scope.
Focused audit for startups and small teams.
Full-scope audit for growing companies.
Multi-entity, multi-country audit programs.
What changes the price? The number of entities and environments, system complexity, access to evidence, frameworks, testing depth and reporting requirements. Employee counts help size the engagement; they are not the only pricing factor.
What changes the timeline? Essentials targets 14 days from kickoff when agreed access and evidence are ready. Broader or multi-entity work is scheduled separately. Your proposal confirms the delivery date and dependencies.
How do you get a fixed proposal? Send a short description of the environment and the reason for the audit. We clarify the scope by email or a scheduled meeting and provide the agreed work, outputs, fee and terms in writing.
06 / PROCESS
Describe the systems, business question and deadline. We agree the boundaries, deliverables, price and delivery date.
We examine configuration, records and procedures, speak with the people responsible and perform the authorised checks in scope.
Findings connect the observed weakness to its risk, the affected control and the action needed. We clarify factual issues with your team.
You review the agreed reports and priorities with us. Payment and follow-up support follow the written terms of your package.
A customer may need evidence before signing a contract. A board may want an independent assessment of security posture. Your IT team may need a clear view of which weaknesses matter most. Tell us what prompted the audit so the scope and reporting answer that decision.
Get Your Audit Scope & Price07 / QUESTIONS BEFORE YOU BUY
The Essentials Audit starts at $5,000, Comprehensive at $12,000 and Enterprise at $25,000, all in USD. Starting prices are subject to scope. The number of environments, entities, systems and frameworks, the depth of testing and the reporting requirements determine the fixed proposal. We agree the fee before work begins.
The Essentials package targets delivery within 14 days of kickoff once the agreed access and evidence are available. Broader Comprehensive and Enterprise engagements can take longer. Your proposal states the delivery date and dependencies; the 14-day target is not a promise for every environment.
Essentials includes an executive summary and a prioritised remediation list for the agreed environment and framework. Comprehensive and Enterprise add detailed technical reporting, an Information Security Program Plan and mapping to the agreed frameworks. Consulting sessions and follow-up support are listed in the package. Your scope document confirms the exact outputs.
Yes. Atlant Security provides an external review of the systems and controls agreed in the scope. Alexander Sverdlov leads the engagement. We review the evidence behind a control, document gaps and explain the business risk and practical next steps. The engagement does not depend on buying a security product from us.
The scope can cover identities and privileged access, endpoints, networks, cloud environments, logging, backups, incident response and security governance. Secure software development and DevSecOps reviews are included in the broader packages where applicable. Essentials covers a single cloud or on-premises environment; a dedicated platform audit can be scoped separately.
No. This is an independent security assessment and gap review. Mapping to an agreed framework supports readiness; it does not issue a SOC 2 report, ISO 27001 certificate or other accreditation. Exploit-based penetration testing is a separate engagement. We identify any additional work in the proposal rather than treating it as automatically included.
Yes. Tell us who needs the results and what decision they must make. We can prioritise exposure, board reporting, supplier due diligence or a customer security review within the agreed scope. A customer questionnaire is one use case, not a prerequisite for commissioning an audit.
You can start with the enquiry form and continue by email, or choose a scheduled online meeting. No telephone number is required. Scope, price, delivery date and payment terms are agreed in writing before work begins. You review the audit report before payment under those agreed terms.
PREFER A SCHEDULED MEETING?
Choose a convenient time for a 30-minute online scoping meeting. You can also send your requirements by email using the form.