Compliance & Framework Readiness
Get SOC 2 Certified in 90 Days. Close the Deal You Have Been Waiting For.
Most SOC 2 consultants quote you 12-18 months and $80,000+. We get growing SaaS and technology companies to SOC 2 Type I readiness in 60-90 days - and our clients pass the audit on the first attempt. Every time.
You see the full readiness report before you pay - We collaborate directly with your auditors
Zero-Risk Guarantee: You review the full readiness report before you pay. If you don't think it's worth it, you pay nothing. No invoice, no awkward conversation.
We take a limited number of new SOC 2 engagements per quarter. Current availability: Q2 2026. If your deal is stalled now, every week you wait is another week procurement doesn't move.
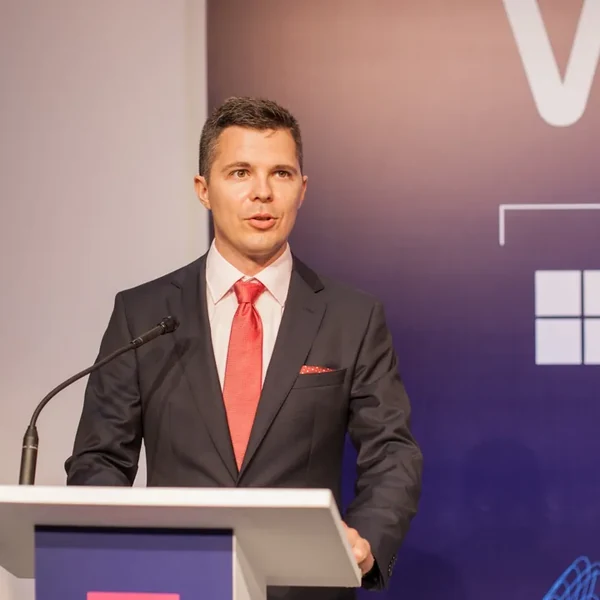
Led by Alexander Sverdlov
Former Microsoft Security Consulting team member. CISSP, CEH, CHFI and Mandiant certified. Secured nuclear energy infrastructure at Emirates Nuclear Energy Corporation. Has personally led 200+ security assessments across 14 countries since 2013. Every SOC 2 engagement at Atlant Security is led directly by Alexander - not delegated to junior staff.
Connect on LinkedIn01 / THE DETAIL
The Three Reasons Companies Come to Us for SOC 2
Specific, urgent, business-critical situations where SOC 2 is the only path forward.
The Enterprise Deal is Stalled
Your prospect sent a 150-question security questionnaire. Procurement will not approve the contract without SOC 2. The deal is stuck and every week it sits there, the risk of losing it grows.
Investors Require It Before Funding
Your Series B investors want to see SOC 2 before the round closes. They need assurance that you can protect customer data at scale. The clock is ticking on the term sheet.
Entering a Regulated Market
You are expanding into healthcare, government, or enterprise markets where SOC 2 is a procurement requirement - not a nice-to-have. No report, no RFP response.
02 / THE DETAIL
What Is SOC 2?
Not a certificate you hang on the wall. A report a licensed CPA firm signs, that your customers read in detail.
SOC 2 (Service Organization Control 2) is an auditing framework developed by the AICPA that evaluates how a technology company manages customer data based on five Trust Service Criteria: Security, Availability, Confidentiality, Processing Integrity, and Privacy.
A SOC 2 report is the document your customers, investors, and partners use to verify that your company handles their data responsibly. It is not a certification you hang on the wall - it is a living audit report produced by a licensed CPA firm that your stakeholders read in detail.
For SaaS companies, cloud service providers, and any business that stores or processes customer data, SOC 2 has become the de facto standard for demonstrating security maturity in B2B sales. An increasing number of enterprise procurement teams will not advance a deal without a current SOC 2 report.
Unlike automated tools like Vanta, Drata, or Tugboat Logic, our assessment is conducted by an experienced expert who knows what auditors actually test. Those platforms are excellent for evidence collection post-implementation, but they cannot independently assess control design correctness, change management adequacy, or vendor risk management.
03 / THE DETAIL
The Five Trust Service Criteria
Only Security is mandatory. The other four get added when a customer contract names them, and each one you add widens the scope of the audit, so add them deliberately rather than by default.
SOC 2 is built around five criteria. Security is mandatory for every report. The other four are selected based on your business model and customer requirements.
Security (CC1-CC9)
MandatoryProtection against unauthorized access and disclosure. Every SOC 2 report includes the Security criteria - it covers access controls, risk management, change management, system monitoring, and incident response. This is the non-negotiable foundation.
Availability
Recommended for SaaSSystems are available for operation as committed. Include this if you have uptime SLAs, status pages, or if your service being down means your customer cannot operate. Most SaaS companies include Availability.
Confidentiality
If handling classified dataInformation designated as confidential is protected. Include this if customers share sensitive business data with you - financial records, IP, proprietary information - and you have contractual obligations to protect it.
Processing Integrity
For financial/transactional systemsProcessing is complete, valid, accurate, and authorized. Include this if your system processes financial transactions, calculations, or data transformations where accuracy is contractually required.
Privacy
For personal data / GDPR / CCPAPersonal information is collected, used, retained, and disclosed in conformity with commitments. Include this if you process personal data and need to demonstrate GDPR or CCPA alignment through your SOC 2 report.
Most SaaS companies start with Security only or Security + Availability. We help you decide which criteria to include during the free strategy call.
04 / THE DETAIL
SOC 2 Type I vs Type II - Which Do You Need?
Type I gets you in the door. Type II keeps you there. Most companies start with Type I and move to Type II within 12 months.
| Type I | Type II | |
|---|---|---|
| What it evaluates | Design of controls at a specific point in time | Operational effectiveness of controls over 6-12 months |
| Timeline | 4-8 weeks after readiness | 6-12 month observation period after Type I |
| Auditor effort | Reviews control design and documentation | Tests controls with evidence samples across the period |
| Customer acceptance | Acceptable for initial sales, early-stage deals | Required by enterprise customers and investors |
| Cost | $15,000-$30,000 (audit only) | $25,000-$50,000 (audit only) |
| Recommended for | First SOC 2, urgent deal requirements | Long-term enterprise sales, Series B+ |
05 / PROCESS
SOC 2 Readiness Timeline
From first call to audit-ready. Our assessment takes just 1 week, with your full readiness roadmap delivered within 5 business days.
Assessment Sessions
2-3 business days of working sessions with your management, IT, and engineering teams across all control areas.
Gap Analysis & Roadmap
Full readiness report plus a priority-based security plan with changes scheduled by category and urgency.
Control Implementation
We implement controls, build policies, prepare documentation, and set up evidence collection.
Type I Audit
We participate in all calls with your auditor - direct collaboration is why our clients pass first time.
06 / PROCESS
How Our SOC 2 Readiness Works - 4 Steps
Gap assessment, remediation with your team, evidence collection, then the handover to the auditor. We stay through fieldwork rather than disappearing once the roadmap is written.
A structured process that produces audit-readiness with minimum disruption to your engineering team.
Free Strategy Call
30 minutes with Alexander directly. We discuss your company, timeline, and why you need SOC 2. You receive an honest assessment of what is involved.
Readiness Assessment
Working sessions with your management, IT, and engineering teams across all control areas. Data collection takes 2-5 business days.
SOC 2 Security Plan
One week after assessment: your full readiness report plus a priority-based security plan with changes scheduled by category and urgency.
Implementation & Audit Support
We implement controls, build policies, prepare documentation, and participate in auditor calls to ensure every finding is addressed.
07 / PRICING
SOC 2 Readiness Pricing
Fixed-price proposals within 24 hours of your strategy call. No hourly billing.
Readiness Assessment
Comprehensive gap analysis and readiness roadmap.
- SOC 2 Gap Analysis
- Control Mapping
- Policy Templates
- Remediation Roadmap
- Evidence Requirements Guide
Zero-risk: You review the report before you pay.
Full Readiness + Implementation
End-to-end: from gap analysis to passing the audit.
- Everything in Readiness Assessment
- Control Implementation
- Policy Build-Out (24+ policies)
- Evidence Collection Setup
- Auditor Coordination
- Mock Audit
- Participation in All Auditor Calls
Zero-risk: You review the report before you pay.
The SOC 2 audit itself (conducted by a licensed CPA firm) typically costs $15,000-$50,000. We help with auditor selection and negotiate on your behalf.
08 / THE DETAIL
Who Needs SOC 2 Readiness?
If any of these describe your situation, SOC 2 readiness is your next step.
09 / THE DETAIL
Why Companies Choose Atlant Security for SOC 2
10 / THE DETAIL
What Clients Say
“Not only did they help us get compliant with strict vendor procedures in a rapid timeframe, but in comparison to many other security vendors, they genuinely cared and invested in full security, not just compliance.”
“We were 6 weeks into a stalled enterprise deal - procurement wouldn't move without SOC 2. Alexander's team completed our readiness assessment in 11 days and had us Type I certified in 67 days. The deal closed for $420K ARR two weeks after we delivered the report.”
“Our investor required SOC 2 Type II before our Series B close. We had zero security policies and AWS logging was completely off. Atlant built everything from scratch - policies, controls, evidence collection - and we passed on the first attempt. We raised $18M.”
“What sold me was the pay-after-delivery model. Every other firm wanted $12K upfront just for the assessment. Alexander said 'review the report first, then decide.' The report was so detailed our auditors said it was the most thorough readiness assessment they'd seen.”
11 / THE DETAIL
Stop Losing Deals Over SOC 2. Get Audit-Ready.
Get Your Roadmap with Alexander. We will discuss your company, timeline, and exactly what is required to pass your SOC 2 audit. Fixed-price proposal delivered within 24 hours.
Zero-risk: You review the report before you pay.
12 / THE DETAIL
Get Your SOC 2 Roadmap
Choose a time for your scoping call.
13 / THE DETAIL
Case Study: From Zero Policies to SOC 2 Type I in 87 Days
A 22-person Series A SaaS company had an enterprise deal stalled in procurement for 6 weeks. The buyer required SOC 2 Type I before signing.
Starting State
- No formal security policies
- No incident response plan
- AWS environment with no logging enabled
- No access control documentation
- Zero prior security assessments
What We Did
- Completed gap assessment in 8 days (identified 47 control gaps)
- Built 24 security policies from scratch
- Implemented AWS CloudTrail, GuardDuty, and Config
- Deployed endpoint protection and MFA across all systems
- Created evidence collection framework for 85 controls
- Coordinated with CPA firm and participated in all auditor calls
Result: Passed SOC 2 Type I on the first attempt, 87 days after engagement start. The stalled enterprise deal closed for $340,000 ARR two weeks after the report was delivered.
Also pursuing NIST 800-171 or CMMC? Many controls overlap with SOC 2. If you serve US federal agencies or defense contractors, we can assess SOC 2 alongside NIST 800-171 or CMMC requirements in a single engagement - reducing duplicate effort and cost. Ask us about combined assessments.
For small projects and ad-hoc work outside our pre-agreed packages or retainers, our standard hourly rate is $460.
14 / FAQ