Executive summary
The most important risks, their business implications and the decisions that need an owner.
CLOUD SECURITY / AMAZON WEB SERVICES
Find the gaps in your AWS environment.
Get a practical plan to close them.
Independent review of your cloud configuration, access and security controls. We explain what is exposed, why it matters and what your team should fix first.
AWS Well-Architected Security Pillar
CIS AWS Foundations Benchmark
01 / WHAT YOU RECEIVE
Every package includes a report and a walkthrough. The depth of testing, accounts, regions and services are agreed in your proposal.
The most important risks, their business implications and the decisions that need an owner.
Risk-ranked findings with the affected accounts or resources, supporting evidence and assessment limitations.
Prioritized actions with relevant AWS configuration or policy changes, so your team knows where to start.
A session with your team to explain the findings, discuss trade-offs and agree the next steps.
02 / FIXED-SCOPE PRICING
Choose by the complexity of your AWS environment. These are starting prices in USD for a one-time audit. We confirm the final scope, price and delivery date in writing before work begins.
FOCUSED ENVIRONMENT
From $2,400
A focused assessment for a straightforward single-account environment.
BROADER COVERAGE
From $4,750
For a more complex account or an agreed group of connected AWS accounts.
COMPLEX ESTATE
Custom
For larger AWS Organizations, complex workloads or specific assurance requirements.
What changes the price? Account and region count, resource volume, services in use, cross-account dependencies, evidence availability and the depth of review. A single complex account may need an expanded or custom scope. No package implies unlimited accounts or resources.
Implementation, retesting, penetration testing and ongoing monitoring are separate unless explicitly included in your proposal. Out-of-scope advisory work is available at the existing rate of $460/hour, with approval before work starts.
03 / ASSESSMENT SCOPE
We use the AWS Well-Architected Security Pillar and applicable CIS AWS Foundations checks to guide the assessment. We agree which areas apply to your environment and package; unused services and excluded accounts are recorded in the scope.

Root account protection, MFA, IAM Identity Center, user lifecycle, role trust, permission boundaries and effective access to sensitive resources.
VPC segmentation, security groups, administrative access, public endpoints and the routes through which workloads can be reached.
S3 bucket and access policies, database exposure, snapshots, KMS key permissions, encryption settings and backup protections.
Applicable EC2, Lambda or container settings, instance metadata, execution roles, secret storage and credentials used by deployment pipelines.
CloudTrail coverage and log protection, Security Hub CSPM and GuardDuty configuration, alert routing and responsibility for investigating findings.
Applicable AWS Organizations policies, cross-account trust, centralized security services, backup arrangements and incident response responsibilities.
We assess the AWS configuration and controls you manage. This is not an attack on AWS infrastructure, a guarantee of finding every vulnerability or a penetration test of your application.
Before a customer security review, after rapid cloud growth or a migration, ahead of an assurance audit, or when you need an independent view of your exposure. We can support readiness for SOC 2 or ISO 27001; certification and formal attestation are separate engagements.
04 / ILLUSTRATIVE REPORT
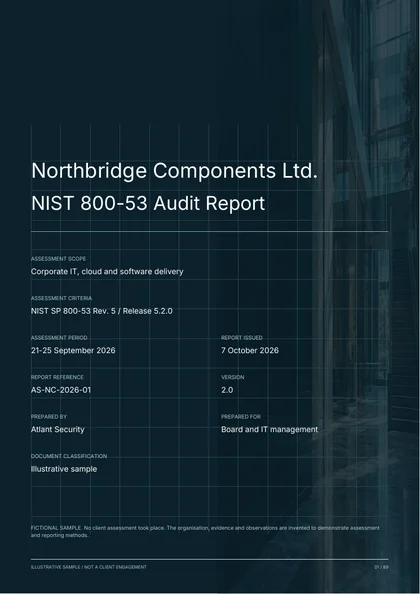
Preview the depth and format of our reporting with a wider IT audit example that includes AWS. The sample contains evidence, risk-ranked findings, diagrams and a remediation plan.
Illustrative NIST SP 800-53 report. The organization, evidence and findings are fictional.
This is a broader IT assessment, not an AWS-only report or the scope of the $2,400 base audit.
A free PDF. Enter your email and company name, and we’ll email you a download link.
05 / HOW IT WORKS
Tell us your account and region count, main AWS services and assessment goals. We confirm coverage, evidence requirements, a fixed price and delivery date.
We work through the agreed controls over screen share. Your AWS or DevOps team operates the console and supplies agreed evidence. You keep your credentials.
We document findings and remediation steps, then walk your team through the results. Review the report before payment; agree any implementation support separately.
A straightforward base audit typically takes about one week from the first assessment session to the report, subject to team availability and complete evidence. Larger reviews receive their own delivery schedule in the proposal.
06 / YOUR QUESTIONS
The base AWS audit starts at $2,400 USD, the expanded audit at $4,750 USD, and enterprise assessments are quoted individually. These are one-time starting prices. We agree the accounts, regions, services, resource sample, deliverables and fixed price in writing before work starts. You review the report before payment.
A focused review of a straightforward single-account environment: agreed identity and access controls, external exposure, core storage, network, logging and encryption settings. You receive an executive summary, evidence and risk-ranked findings, a prioritized remediation plan and a walkthrough. The proposal records the account, regions, resource sample and exclusions. A complex single account may require an expanded scope.
No. We conduct the assessment through screen-sharing sessions with your AWS or DevOps team. Your team operates the console and supplies agreed evidence. You retain control of your credentials and environment throughout the review.
Security Hub CSPM performs automated configuration checks, including checks for overly permissive IAM policies and public S3 access. GuardDuty detects suspicious activity and threats. We use their findings where available, then review permissions, architecture, business context and operational responsibilities within the agreed scope. The report explains which risks matter to your environment and how to remediate them.
A straightforward base audit typically takes about one week from the first assessment session to the report, subject to team availability and complete evidence. We agree the delivery date before starting. Larger multi-account or complex reviews receive a separate schedule in the proposal.
Yes. Expanded and enterprise scopes can include agreed accounts and organizational units, service control policies, cross-account role trust, central logging, and delegated security services. We agree account coverage and sampling before quoting; the starting price is not an unlimited-account offer.
The assessment reviews AWS configuration and security controls. Exploitation-based testing of applications or cloud resources, implementation of fixes, retesting and ongoing monitoring are separate unless expressly included in the proposal. We can scope follow-up work after discussing the findings.
No. The assessment can identify AWS control gaps and provide evidence to support readiness. A SOC 2 attestation or ISO 27001 certification has its own scope, process and qualified assessor. We agree any required control mapping before the assessment.
No. It is an illustrative NIST SP 800-53 report for a fictional organization, with an AWS assessment alongside other IT security work. It shows how findings, evidence and remediation can be presented. Your AWS report covers the environment and deliverables agreed in your proposal; the wider sample does not define the $2,400 package.