Identity & membership
Sign-in, invitations, organization membership, role changes and offboarding. Test the permissions of guests, members, administrators and former users.
FOR SAAS FOUNDERS & ENGINEERING TEAMS
From $6,000 USD · Scope your audit ↗
Find out whether one customer can access another customer’s data.
Independent testing of your Supabase application, database access rules, files and server-side functions. Get verified findings, practical fixes and a retest of the agreed remediation.
01 / WHAT WE ASSESS
Your application’s permissions must hold across database queries, stored files, functions and background jobs. We agree the roles and data paths, then test the intended boundaries.

Sign-in, invitations, organization membership, role changes and offboarding. Test the permissions of guests, members, administrators and former users.
Policies and database grants for read, create, update and delete operations. Review views, RPCs and privileged database execution paths.
Follow customer identifiers through APIs, exports, background jobs and administrative actions. Use separate test organizations to check cross-customer access.
Upload, listing, replacement and download permissions. Review public files, signed links and the relationship between file access and organization membership.
Authentication and authorization in server functions, webhook callers, administrative credentials and exposed secrets. Check permission decisions before privileged operations.
Agreed customer-owned hosting, deployment identities, repository access and critical integrations. Include source-assisted review where specified in the proposal.
We assess your implementation and explicitly authorized assets. Provider infrastructure and unrelated third-party systems are outside scope. Test data, permitted actions and operational limits are agreed before testing.
02 / TEST THE BUSINESS RULES
Trace the request from the user to the export job and final download. Test the complete action with synthetic data.
Check the requesting role, selected organization and object permission before the function retrieves or changes records.
Review sessions, background tasks and existing links against the agreed offboarding rules.
The review combines relevant platform guidance, configuration and source review where agreed, and manual testing. We record what was tested, what was unavailable and what remains outside the assessment.
03 / WHAT YOU RECEIVE
The agreed permissions, tested paths and observed results for your customer organizations and roles.
Affected functions and data paths, reproducible steps, redacted evidence and the reason each issue matters.
Concrete engineering changes ordered by risk, with scope limitations and untested areas recorded.
Review the report with your team. One retest of reported findings within 30 days is included in the agreed scope.
04 / SUPABASE SECURITY AUDIT PRICING
Tell us what you operate and which security decisions the review needs to support. We confirm the tests, deliverables and schedule in writing.
From $6,000 USD
One application or agreed environment, with a bounded set of features and integrations. One retest of reported findings within 30 days of report delivery is included.
Get Your Supabase Audit ScopeLarger environments and multiple applications are quoted separately. Remediation implementation, recurring monitoring and new features are separate work unless included in your proposal.
Your proposal sets the test window and report date. Timing depends on scope and access readiness.
05 / ILLUSTRATIVE REPORT
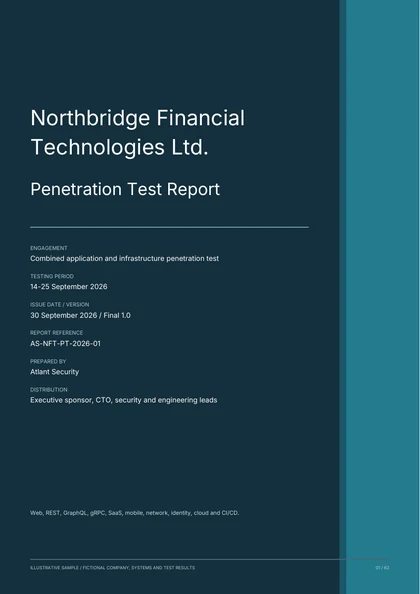
Preview the reporting format: technical findings, reproducible evidence and remediation. This combined example covers several penetration-testing disciplines.
Fictional organization and findings. This is a combined pentest example, not a Supabase client report or the scope of the $6,000 starting engagement.
Request it with your work email. We will email you a download link.
A free PDF. Enter your email and company name, and we’ll email you a download link.
06 / WORKING TOGETHER
Share your architecture, roles, integrations and deadline. We agree targets, permissions, test accounts and safe operating limits.
Review the agreed controls and test the relevant failure cases. We escalate urgent findings and document reproducible evidence.
Walk through the report, assign remediation priorities and use the included retest to check reported findings after correction.
DEFINE YOUR SCOPE
Describe your application, customer roles and data paths. Complete one request and send the full scope to your inbox and Atlant Security.
REQUEST RECEIVED
Reference: . Email copies are being sent to and Alexander at Atlant Security. Check your spam folder if needed.
You can also book a call to discuss the scope.
PREFER A CONVERSATION FIRST?
Book a 30-minute online meeting, or use the builder above for a written request.
07 / BEFORE YOU START
Engagements start at $6,000 USD for one application and an agreed set of roles, data paths and functions. We confirm the scope, exclusions, schedule and fixed price before work begins. Larger applications and additional environments are quoted separately.
No. The agreed assessment combines policy and configuration review with manual testing of application permissions, customer isolation, files and server functions. The proposal identifies the specific features and integrations included.
We normally need an architecture outline, role list and suitable accounts in at least two test organizations. Source code, database policies and read-only configuration access improve the review where agreed. Use synthetic customer records and files.
Yes, where the application and its Supabase implementation are within the agreed scope. We assess the deployed permissions and data flows, regardless of how the application was built.
The report documents the work, findings, limitations and retest results. Share the buyer’s requirements before scoping so we can assess the requested areas. Acceptance remains the buyer’s decision; this is not a Supabase certification.
The engagement includes remediation guidance and one retest of the reported findings within 30 days of report delivery. Implementing fixes, testing new features or adding environments is separate work unless included in the written proposal.
08 / FOR YOUR TEAM
Explore the access rules, test scenarios and evidence to prepare before the review.