Installation & identity
Installation and authorization flows, request authentication, token handling, scope changes, uninstall behavior, account recovery and support access. Each entry point needs the right proof of identity.
FOR SHOPIFY APP DEVELOPERS & PRODUCT TEAMS
From $7,000 USD · Scope your test ↗
Find the paths from one vulnerable app to your merchants’ data.
Independent vulnerability assessment and penetration testing of your Shopify app, APIs and agreed hosting environment. Get verified findings, reproducible evidence and fixes your developers can implement.
Public and custom apps · Embedded apps · App backends & APIs
01 / WHAT WE TEST
A store can run on Shopify while an app’s backend, database and deployment pipeline sit elsewhere. We assess the parts you operate and the ways they handle merchant access and data.

Installation and authorization flows, request authentication, token handling, scope changes, uninstall behavior, account recovery and support access. Each entry point needs the right proof of identity.
Cross-store access to records, exports, files and background jobs. We test whether a valid user or app installation can reach another merchant’s data or perform actions beyond its role.
Your REST and GraphQL endpoints, object and function authorization, input handling, uploads and server-side URL fetching. Agreed workflows can include billing, discounts, inventory and bulk operations.
Webhook authenticity and duplicate handling; app-proxy permissions; extension-to-backend requests; stored content and settings rendered on storefronts. We check the path from incoming data to its effect.
Agreed app-owned hosts, cloud identities, storage exposure, secrets, network boundaries and origin protection. We assess what the WAF enforces and what still needs application-level authorization.
Source-assisted review can trace sensitive logic, dependencies, CI/CD permissions, deployment secrets and artifact controls. Repository and cloud access, review depth and sampling are agreed in the proposal.
Testing covers your app and authorized assets. It does not authorize attacks on Shopify infrastructure, unrelated merchants or third-party providers. We agree test stores, accounts, data, rate limits and exclusions before work starts.
02 / HOW WE FIND MEANINGFUL RISK
VAPT combines vulnerability assessment with manual penetration testing. Automated checks help find exposure; targeted testing establishes whether a weakness can cross a real trust boundary.
Follow the request through authorization, database queries, asynchronous jobs and file delivery. Verify both permitted access and expected denials using separate test stores.
Trace settings and stored content from app endpoints to storefront rendering. Check whether a signed request is being mistaken for permission to perform an administrative action.
Where authorized, examine how application access connects to secrets, service identities and release systems. Stop at agreed safety limits and document untested steps.
Test selection draws on OWASP WSTG, ASVS, the OWASP API Security Top 10 and Shopify’s app security guidance. The agreed scope determines coverage; these are testing references, not a certification claim.
03 / WHAT YOUR TEAM RECEIVES
Business impact, affected boundaries and the highest-priority risks, with the scope and limitations stated clearly.
Affected assets, reproduction steps, sanitized evidence, severity rationale and specific remediation guidance.
What was tested, what could not be tested and why. Prioritized actions help engineering plan the work.
A session to review the findings with your team. Any remediation retest, its window and depth are agreed in the proposal.
04 / SHOPIFY APP VAPT PRICING
Tell us what your app does, how it is hosted and what needs testing. We confirm the targets, approach, deliverables and schedule in writing before the engagement.
From $7,000 USD
One-time starting price, not a monthly retainer.
Get My App VAPT Scope & PriceThe starting price is for a bounded engagement. It does not include every category above without limit. We identify the included tests, exclusions and any separately priced work in your proposal.
Remediation implementation, recurring monitoring and third-party assurance or certification are separate services.
05 / ILLUSTRATIVE REPORT
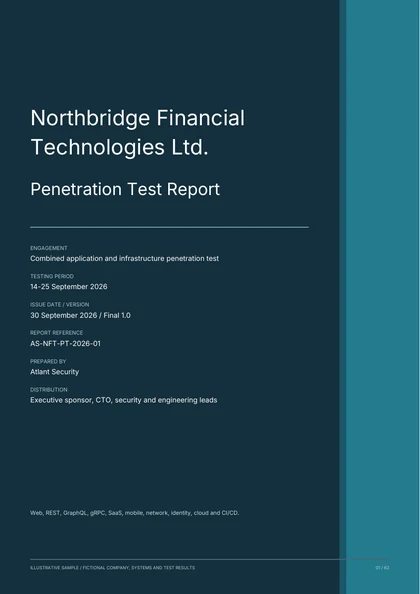
See how we present technical findings, reproducible evidence and remediation. This combined sample includes web, API and SaaS isolation testing alongside other disciplines.
62 pages. 24 findings. 14 charts, diagrams and matrices.
Fictional organization and findings. This is a combined pentest example, not a Shopify client report or the scope of the $7,000 engagement.
A free PDF. Enter your email and company name, and we’ll email you a download link.
06 / WORKING TOGETHER
We map the app, data flows and priorities. Agree ownership permissions, two test stores where isolation is in scope, roles, testing windows and escalation contacts.
Review the agreed attack surface and exercise relevant failure cases. Validate findings, avoid unnecessary access to real customer data and escalate urgent issues through the agreed channel.
Deliver the report and walk through remediation priorities. Confirm any limitations and the evidence needed to verify fixes within the agreed retest scope.
Timing depends on scope and access readiness. Your proposal includes the test window and report date; we do not promise the same turnaround for every app.
DEFINE YOUR SCOPE
Start with your app and APIs; add cloud testing if needed. Include your app URLs, merchant roles, test stores and hosting details. Your completed request is sent to you and Atlant Security.
REQUEST RECEIVED
Reference: . Email copies are being sent to and Alexander at Atlant Security. Check your spam folder if needed.
You can also book a call to discuss the scope.
PREFER TO DISCUSS IT FIRST?
Use the RFP builder for a written request, or choose a 30-minute online meeting with Atlant Security.
07 / QUESTIONS BEFORE YOU START
Vulnerability Assessment and Penetration Testing examines the security of a Shopify app and its agreed supporting systems. We combine exposure and configuration review with manual tests of authentication, authorization, store isolation, APIs and business logic. The report distinguishes verified findings from limitations and areas that were not tested.
Pricing starts at $7,000 USD for a one-time, scoped engagement. The final quote depends on functionality, roles, APIs, integrations, hosting coverage, source review and retest requirements. We agree the included work and a fixed price before starting; the starting price is not an unlimited full-stack assessment.
This service is for teams developing or operating public or custom Shopify apps. A merchant looking to secure store administration, installed apps, Google Workspace or advertising accounts should use our ecommerce cybersecurity service. We can clarify the correct scope before quoting.
No. The engagement covers your app and explicitly authorized assets. Test stores and accounts must be approved for the work. Shopify infrastructure, other merchants and third-party systems are outside scope unless separate, valid authorization and applicable provider rules permit the activity.
Yes, when included in the agreed scope. Hosting review can cover cloud identities, exposed services, storage, network rules, secrets and origin protection. Source-assisted work can examine sensitive code paths and build or deployment controls. Read-only evidence review and active exploitation are different activities and are identified separately in the proposal.
Two isolated test stores are useful for testing cross-store access. We also need suitable accounts for the roles in scope, realistic test data and the relevant API documentation. Where access is unavailable, we agree an alternative and record any resulting limitation.
No. A WAF can filter some malicious requests, but it generally cannot determine which merchant owns a record or which business actions a role should perform. We test with agreed production-like defenses and, where separately authorized, can compare behavior through controlled access to the origin.
Retest scope, timing and pricing are specified in your proposal. You receive an independent assessment report, not Shopify approval, PCI certification or a guarantee that no vulnerabilities exist. Any customer-facing summary or completion statement must accurately describe the work and its limitations.
Complete the RFP builder on this page or book an online scoping call. We agree the app, environments, access, test window and report date before work starts. The schedule depends on scope and access readiness rather than a universal turnaround promise.
No. It is an illustrative, combined penetration test report for a fictional organization. It demonstrates reporting depth across web, API, SaaS and other systems; it is not a client case study or the promised scope of the $7,000 starting engagement. We email the download link after you request it with your company email.
08 / FOR YOUR ENGINEERING TEAM
Understand the controls across your app’s architecture and operations.
PENETRATION TESTINGPrepare the assets, roles and workflows for a useful test.
SECURITY AUDITSee how a wider review connects implementation to security controls.
Looking for security help with your store rather than an app you develop? See ecommerce cybersecurity services.