Atlant Security delivers ecommerce cybersecurity solutions for Shopify, WooCommerce, Adobe Commerce (Magento), BigCommerce, and custom stores. We assess payment flows, application and API security, third-party access, and the controls protecting your customer data.
Get a prioritized remediation plan with clear findings and practical fixes. Security audits start at $5,000; ongoing vCISO support starts at $3,300 per month. Your scope and price are agreed before work begins.
Payment processing and PCI DSS compliance
Shopify, WooCommerce, Magento, and custom platforms
Fixed pricing - pay after you approve the report
PCI DSSSOC 2GDPRCCPAISO 27001NIST 800-53
CLIENT EXPERIENCE / RHO NUTRITION
Securing the business behind the store.
Atlant Security secured Rho Nutrition’s cloud systems, advertising and Meta accounts, Google Workspace, and all administrator access to Shopify.
Security across the cloud services used to run the business.
Advertising & Meta accounts
Protection for the accounts supporting customer acquisition and the brand’s presence.
Google Workspace
Security for the company’s workspace and the access behind everyday collaboration.
Shopify administrator access
Securing all administrator access to the online store.
01 / THE BUSINESS RISK
Reduce the risks that interrupt sales and damage trust
A compromised online store can expose customer records, enable fraudulent transactions, and interrupt order processing. The assessment connects technical weaknesses to those business outcomes.
01
Payment abuse
Card testing, manipulated prices, unauthorized refunds, and checkout skimming require different controls. We identify the paths that matter for your payment flow.
02
Account and data exposure
Customer account takeover and excessive staff or app permissions can expose orders, addresses, exports, and administrative functions.
03
Interrupted trading
Fragile integrations, unsafe releases, and untested recovery procedures can turn an incident into extended downtime. We examine the dependencies behind your storefront.
02 / WHAT WE SECURE
What our ecommerce security solutions cover
We scope the work around your storefront, checkout, customer accounts, back-office systems, and integrations. Existing security products are assessed in context, with recommendations based on the gaps we find.
01
Payment pages and e-skimming
What we assess and improve
Payment data flows, third-party scripts, tag-manager access, script integrity, and unauthorized changes to checkout.
What you receive
A map of payment dependencies, configuration gaps, and controls to strengthen payment-page protection.
02
Checkout and transaction abuse
What we assess and improve
Cart pricing, discount stacking, refunds, gift cards, payment status, and order processing using agreed test transactions.
What you receive
Reproducible findings explaining how a workflow can be abused and the server-side checks needed to fix it.
An inventory of risky dependencies, excessive access, and configuration changes to prioritize.
07
Customer data and recovery
What we assess and improve
Data exports, retention settings, backup access, restoration procedures, security logs, and incident-response responsibilities.
What you receive
A remediation plan connecting data protection, recovery readiness, and assigned control owners.
03 / BUILT AROUND YOUR PLATFORM
Security for your ecommerce platform
The boundary between platform security and merchant responsibility changes with your architecture. We identify what your team controls and what depends on the platform, host, or payment provider.
01
Shopify and Shopify Plus
Staff and collaborator access, app permissions, custom themes, checkout extensions, integrations, and API credentials. Reviews focus on your merchant configuration and custom components.
02
WooCommerce
WordPress and plugin exposure, payment integrations, administrator access, REST API permissions, hosting configuration, backups, and the process for applying updates safely.
03
Adobe Commerce / Magento
Custom modules, extensions, checkout scripts, GraphQL and REST endpoints, administrator permissions, patch management, and the hosting and deployment environment.
04
BigCommerce
Staff roles, API accounts, installed apps, checkout integrations, storefront customizations, and access to customer and order data.
05
Custom and headless commerce
Storefront and backend trust boundaries, authorization across services, payment webhooks, order workflows, secrets, CI/CD permissions, and cloud infrastructure.
04 / THE ENGAGEMENT
From scoping to a remediation plan
The work starts with your architecture and business priorities. Scope, permissions, test windows, and exclusions are agreed before testing begins.
01
Scope the store
Map domains, applications, APIs, payment flows, integrations, data locations, and access roles. Agree the environments and safe test transactions.
02
Assess and validate
Review configuration and access, then validate weaknesses through agreed manual testing and targeted automated checks. Record evidence and affected assets.
03
Prioritize the work
Rank findings by exploitability and business impact. Separate urgent containment, practical short-term fixes, and changes that need development or supplier support.
04
Support remediation
Walk through the findings with your team. Agree implementation support and retest scope so you know how fixes will be checked.
What the report contains
Scope, tested assets, methodology, and limitations.
Findings with evidence, business impact, and specific remediation actions.
A prioritized work plan that your developers, operations team, and suppliers can act on.
An executive summary and the security decisions requiring business ownership.
Continuous protection also requires operational ownership. Product licenses, managed monitoring, and round-the-clock response are included only when specified in the proposal.
01
Ecommerce security audit
You need an independent picture of your store’s risks.
Review platform configuration, payments, access, integrations, and data protection; deliver a prioritized remediation plan.
02
Scoped penetration test
You need to validate a release, API, or checkout workflow.
Test authorization and business logic using agreed accounts and transactions. Confirm the separate testing scope and retest terms.
03
Control and configuration review
You already have security tools but are unsure whether they work.
Review WAF, bot controls, identity, logging, and alert handling. Define gaps and configuration changes using your chosen products.
04
Ecommerce vCISO support
Security work has no owner between audits.
Provide ongoing leadership for remediation, supplier risk, compliance preparation, and incident planning through an agreed retainer.
Led by Ex-Microsoft Security Team
06 / EXPERTISE. WITH A NAME.
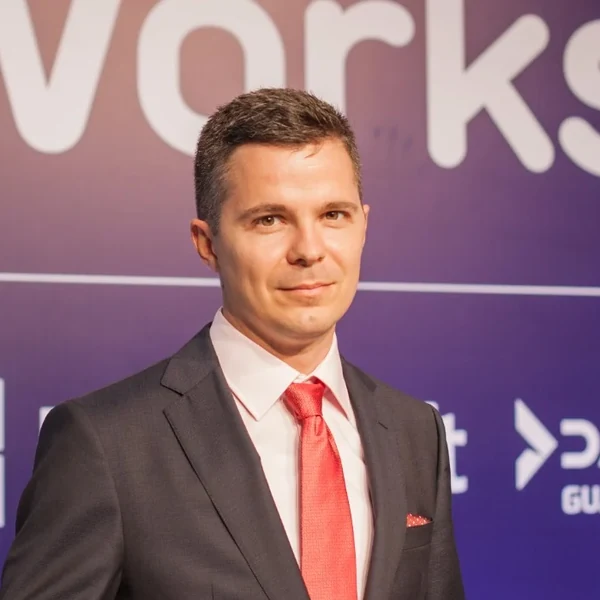
Every Ecommerce Engagement Is Led by Alexander Sverdlov
Former Microsoft Security Consulting team member. CISSP, CEH, CHFI and Mandiant certified. Alexander has personally led 200+ security assessments across 14 countries since 2013, securing banks, government agencies, and nuclear energy infrastructure. He brings that enterprise methodology to ecommerce - payment security, PCI DSS, and the platform-specific vulnerabilities that put your customers at risk - and personally leads every engagement rather than handing it to junior staff.
Your assessment is led by Alexander Sverdlov, with findings explained in terms your developers and business owners can use. We work across the payment flow, application, identities, and integrations, so the scope follows the way your store actually operates.
Former Microsoft Security Consulting team - enterprise expertise applied to your store
Ecommerce-specific methodology - not generic IT security checklists
PCI DSS, SOC 2, and GDPR compliance built into every engagement
Every engagement led personally by founder Alexander Sverdlov
Fixed pricing - you know the cost before we start, pay after you approve the report
Platform experts for Shopify, WooCommerce, Magento, and custom builds
Vendor-agnostic recommendations - we recommend what protects you, not what pays us
07 / PAYMENT SECURITY & ASSURANCE
PCI DSS readiness and payment-page protection
We map how payment data moves through your store, identify the systems that can affect it, and review the evidence behind your controls. Our PCI DSS consulting supports scoping, gap assessment, remediation, and preparation for the applicable validation process.
Checkout scripts and e-skimming
Payment-page protection includes knowing which scripts execute, who authorized them, how integrity is checked, and how unexpected changes are detected. We review script and tag-manager access, dependencies, and the monitoring of security-impacting changes.
Where relevant to your business, the scope can include technical and organizational data-protection controls and evidence needed by enterprise customers. GDPR Article 32 assessments and SOC 2 readiness can be coordinated with the ecommerce assessment. Formal attestation or certification follows the applicable independent assessment process.
08 / YOUR INVESTMENT
Ecommerce Security Pricing
Transparent, fixed pricing. No hourly billing surprises. You receive a detailed proposal before we start, and for assessments, you don't pay until you approve the final report.
Ecommerce cybersecurity solutions: common questions
What are ecommerce cybersecurity solutions?
Ecommerce cybersecurity solutions combine the controls and specialist services that protect an online store: payment-page security, customer and administrator account protection, application and API testing, bot controls, secure integrations, backups, and incident preparation. Atlant Security assesses the gaps in your store, prioritizes remediation, and supports implementation through an agreed project or ongoing vCISO engagement.
Which ecommerce security service should we start with?
Start with an audit when you need a view of risks across your store, integrations, identities, and infrastructure. Choose a penetration test when you need to demonstrate whether a particular application, API, or checkout workflow can be exploited. Ongoing vCISO support provides an owner for remediation, supplier reviews, and security governance. We scope these around your platform, payment flows, and business priorities.
How much do your ecommerce cybersecurity solutions cost?
The Ecommerce Security Audit starts at $5,000 as a one-time engagement. Ecommerce vCISO support starts at $3,300 per month. The final scope and fixed price are agreed before work begins; assessment payment is due after you approve the report. The proposal identifies any separately scoped testing, implementation, or third-party tooling.
Is a WAF or a secure ecommerce platform enough?
A web application firewall and a managed platform address important risks, but neither can establish that a customer is entitled to a particular order, that a refund was correctly authorized, or that an installed app needs access to all customer records. We assess the responsibilities that remain with your business and test controls in your actual configuration.
Do you work with Shopify, WooCommerce, Magento, and headless stores?
Yes. Scope can include Shopify and Shopify Plus, WooCommerce, Adobe Commerce (Magento), BigCommerce, and custom or headless storefronts. For managed platforms, we focus on your accounts, apps, custom code, payment integrations, and configuration. For self-hosted platforms, the scope can also include hosting, patching, databases, and deployment pipelines.
Can you help with PCI DSS and payment-page security?
Yes. We help map payment data flows, determine the assessment scope, identify gaps, and prepare remediation and supporting evidence. Payment-page reviews can cover script authorization, integrity, and tamper detection. The applicable validation method and responsibilities depend on your payment architecture and the requirements of your acquirer or payment brand; formal validation and ASV services are scoped separately where needed.
Can testing take place without disrupting sales?
We agree the environment, test accounts, payment instruments, permitted request rates, exclusions, and escalation contacts before testing. Staging is used where practical, with separately agreed production checks. Destructive tests and denial-of-service testing are excluded unless specifically authorized. Peak trading periods and fragile integrations are considered during scoping.
What do we receive after the assessment?
You receive findings with supporting evidence, affected assets, business impact, and specific remediation guidance, plus a prioritized plan and an executive summary. The proposal defines the walkthrough, implementation support, and retest arrangements. We identify what was tested, what was excluded, and which risks still need a business decision.
What if our store is already compromised?
Contact the incident response team promptly. Preserve logs and coordinate containment with your payment provider, hosting provider, and relevant specialists. Avoid changes that destroy evidence. Investigation, containment, recovery, and a later security assessment are separate stages; the response scope depends on the incident.
Tell us your platform, payment setup, integrations, and the concern you need resolved. We will define the work, deliverables, and fixed price before the engagement begins.