Advisory & CISO Services
Security Advice With No Vendor Commission Sitting Behind It.
Most IT security consulting firms run a security assessment, identify your vulnerabilities, and then sell you the products to address them - earning a commission on every tool they place.
That is not security consulting. That is sales with a security report as the pitch deck. Atlant Security does not sell products, earn commissions, or recommend solutions based on vendor relationships. We assess your environment, build your security programme, and implement the controls that actually protect you, then you pay after you approve the work.
- No products sold, no commissions, no vendor relationship behind a recommendation
- Assessment, programme build and hands-on implementation by the same senior consultant
- You pay after you approve the work
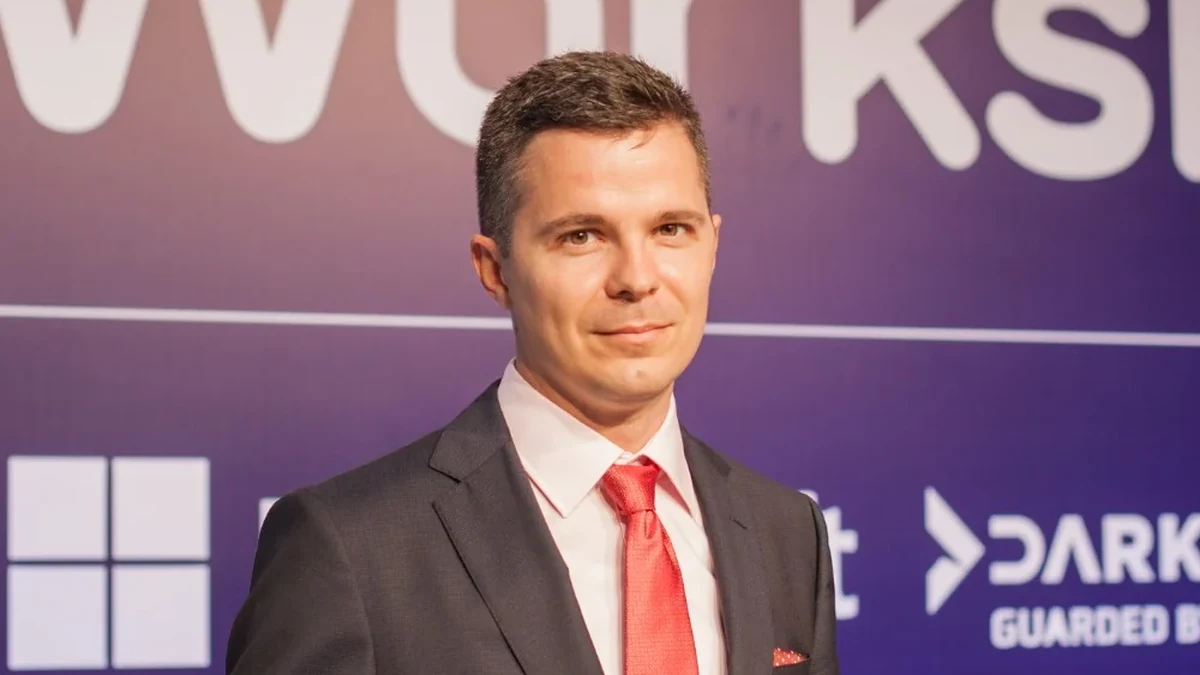
Founded by a former member of Microsoft’s Security Consulting team. The person who scopes the engagement is the person who delivers it.
01 / THE DETAIL
Your IT Security Consultant
Built security programmes for banks, nuclear operators, and government institutions - now bringing that standard to every organisation we work with.
Alexander Sverdlov founded Atlant Security after more than 20 years in information security - including time as part of Microsoft's Security Consulting team and as an independent consultant to banks (SCB in Thailand, Akbank in Turkey), government ministries, and the Emirates Nuclear Energy Corporation.
02 / THE DETAIL
Why Most IT Security Consulting Firms Leave You No More Secure Than When They Arrived
The dominant business model in IT security consulting is built around product sales. A consulting firm conducts an assessment - then recommends the products they are authorised to resell at a 20-40% commission. Their revenue grows when your gaps persist.
The vendor-independence principle - Atlant Security has never earned a commission, referral fee, or reseller margin from any security product vendor. When we recommend a solution, it is the one we believe is correct for your situation - not the one that generates revenue for us.
03 / THE DETAIL
IT Security Consulting Services - What We Actually Do
Eight specific services. Each one is a complete engagement with defined deliverables - not a billable hour with undefined scope. Most engagements combine several services into a single programme.
IT Security Assessment
The foundation of every engagement. We assess your environment against NIST 800-53 and industry best practices across 14 security domains: access control, identity management, cloud configuration, network architecture, endpoint security, and more. Every gap identified, risk-ranked, and paired with a specific fix.
Learn moreInformation Security Programme Build
A security assessment without implementation is just a list of problems. After assessing your environment, we build your complete Information Security Programme - policies, technical controls, monitoring, training, and compliance readiness - implemented with your team, not just documented.
Learn moreVirtual CISO (CISO as a Service)
Ongoing security leadership for organisations that need a Chief Information Security Officer but are not ready to hire one full-time. Strategic planning, compliance management, board reporting, vendor evaluation, and incident response - delivered fractionally.
Learn moreCompliance Programme - SOC 2, ISO 27001, HIPAA
We build the compliance programme your customers, investors, or regulators require - not a documentation exercise, but a functioning security programme that passes audits because the controls actually work.
Learn moreCloud Security Assessment
AWS, Azure, and GCP security configuration review covering every service in your cloud environment. IAM least privilege validation, network configuration, encryption, logging, and storage security.
Learn moreActive Directory and Identity Security
Active Directory is the single most attacked system in any Windows-based organisation. We assess your AD environment across privileged account management, GPO configuration, Kerberos security, trust relationships, and attack path analysis.
Learn moreSecurity Policy and Documentation
The policy suite that SOC 2 auditors, ISO 27001 certification bodies, and enterprise customers expect: Information Security Policy, Acceptable Use Policy, Incident Response Plan, Business Continuity Plan, and more.
Learn moreSecurity Awareness Training
Security awareness training that changes employee behaviour - not a 30-minute compliance video nobody remembers. Custom phishing simulations, role-specific training, and ongoing reinforcement.
Learn more04 / THE DETAIL
Industries We Secure - and the Specific Risks Each One Faces
IT security is not the same problem in every industry. A law firm's most critical risk is client confidentiality. A bank's most critical risk is transaction fraud. We tailor our approach to your industry's specific threat landscape.
Law Firms and Legal Services
Attorney-client privilege is the most valuable asset a law firm has - and the most targeted. We protect law firms from spear-phishing, email compromise, and data exfiltration targeting sensitive case materials.
Financial Services and Banking
We have built security programmes for banks in Thailand, Turkey, and across the Middle East - and for fintechs across the US, UK, and EU. PCI DSS, SOX, GLBA, and DORA compliance expertise.
Software Development and SaaS
Software companies face security from three directions: customers demanding SOC 2, investors requiring a security programme, and their own platform needing protection. We handle all three.
Critical Infrastructure and Industrial
We have worked with nuclear operators and government ministries - environments where the consequence of a security failure is operational disruption of critical services, not just financial loss.
Healthcare and Life Sciences
HIPAA compliance, PHI protection, and operational resilience for clinical systems. Ransomware targeting healthcare has increased dramatically - prevention is the only viable strategy.
Small and Mid-Size Businesses
SMBs are the most targeted and least protected segment. Attackers know that SMBs have valuable data and limited security resources - making them the path of least resistance.
05 / THE DETAIL
What Changes When You Engage Atlant Security
Six specific outcomes. Each one removes a specific obstacle or risk from your organisation.
You know exactly what your security vulnerabilities are
Not a CVSS-sorted list of technical findings. A risk-ranked finding set tied to your specific business, your specific data, and your specific threat profile.
You have a security programme that actually works
Policies written and enforced. Controls documented and implemented. Training scheduled and completed. A real programme, not a compliance exercise.
You pass the compliance audit and win the enterprise customer
SOC 2 Type II, ISO 27001 certification, HIPAA compliance - the specific business outcome your engagement is tied to.
You get vendor-independent advice
When we recommend a security tool, it is because that tool is the right answer for your situation - not because we earn a margin on it.
Your leadership team understands your security risk
Security information translated into business language your CEO and board can understand and act on.
Your security improves continuously
Monthly vulnerability management, quarterly access reviews, annual audits, and continuous threat monitoring - not a once-a-year assessment.
06 / PROCESS
How an Atlant Security IT Consulting Engagement Works
From first conversation to running security programme. No retainer invoice before work begins. No scope creep. No product upsell. Deliverables you approve before you pay.
Free Strategy Call
45 minutes. You describe your current security posture, your business, and the specific outcome driving the engagement - a compliance requirement, a customer request, an incident. We outline exactly what needs to happen, in what order, and what it will cost.
Security Assessment
We assess your environment across all 14 security domains - through interviews with your IT team, review of existing configurations, and technical examination of your infrastructure. Every gap identified, risk-ranked, and paired with a specific remediation.
Programme Build and Implementation
We build your Information Security Programme - policies, procedures, and technical controls - implemented with your team. For compliance engagements, we manage the audit process end to end.
Ongoing Maintenance and Growth
Security is not a project with an end date. We maintain your programme as your business grows - managing annual audits, handling new compliance requirements, responding to incidents, and keeping your security posture current.
No-Risk Guarantee
Every deliverable - assessment report, programme plan, policy document - is reviewed and approved by you before any invoice is issued. If you do not approve the work, you do not pay.
07 / THE DETAIL
The Security Frameworks Atlant Security Assesses Against
Every assessment is structured against established frameworks so your security posture is measured against the standards your customers, regulators, and investors use to evaluate you.
For small projects and ad-hoc work outside our pre-agreed packages or retainers, our standard hourly rate is $460.
08 / FAQ
IT Security Consulting - Frequently Asked Questions
Answered by a former Microsoft Security Consulting expert with 20+ years of experience securing banks, nuclear operators, government ministries, and technology companies worldwide.
What is IT security consulting?
How is Atlant Security different from other IT security consultants?
What industries do you work with?
What does a security assessment include?
Do you sell security products?
How long does an IT security engagement take?
How much do IT security consulting services cost?
What is a Virtual CISO and do I need one?
Can you help after a security breach?
What is the difference between a security assessment and a penetration test?
How do you handle confidential information during an assessment?
09 / THE DETAIL
Know Exactly Where Your Security Stands - and What to Do About It
Free 45-minute strategy call. You describe your situation - we tell you exactly what needs to happen, in what order, and what it will cost. No commitment, no vendor pitch, no pressure.
Free call - No vendor commissions - Pay after approval - 20+ years experience - No long-term contracts