EVERY PACKAGE
Executive summary
The material risks in your agreed scope, explained for the people making business decisions.
INDEPENDENT CYBERSECURITY REVIEW
Understand where your security controls fall short and what to fix first.
Get an independent assessment of your systems, access and security practices, with an executive summary and remediation priorities for your agreed scope.
From $5,000
Led by Alexander Sverdlov200+ assessments · 14 countries
WHAT YOU RECEIVE
Understand your security posture, the gaps that matter and the order to fix them. Choose the reporting depth your team needs.
EVERY PACKAGE
The material risks in your agreed scope, explained for the people making business decisions.
EVERY PACKAGE
What to fix, why it matters and which actions should come first.
COMPREHENSIVE & ENTERPRISE
Documented findings, supporting evidence and an Information Security Program Plan for your team.
The written scope sets the systems, checks and outputs included. See package details →
YOUR AUDITOR
Former Microsoft Security Consulting
CISSP · CEH · CHFI · Mandiant certified
Alexander leads your scope discussion, reviews the controls and explains the findings to your team.
How to get your team behind the changes.
“Alexander is professional, reliable and available. He is clearly an expert in his field. Building trust in cybersecurity is obviously essential and Alexander has constantly demonstrated that my trust is well-placed.”
“The assessment was really imposing and remarkable. It was beyond my expectations, very detailed, and things were very closely inspected and discussed. It was a great experience working with you.”
SEE THE DELIVERABLE
Open six pages: an executive summary, scope, control-family results and a detailed finding with corrective actions.
Open sample excerptIllustrative report. Northbridge Components Ltd. and its findings are fictional.
Every packageExecutive summary & remediation priorities.
Comprehensive & EnterpriseDetailed technical findings & programme plan, within the agreed scope.
89 pages. We’ll email you a download link.
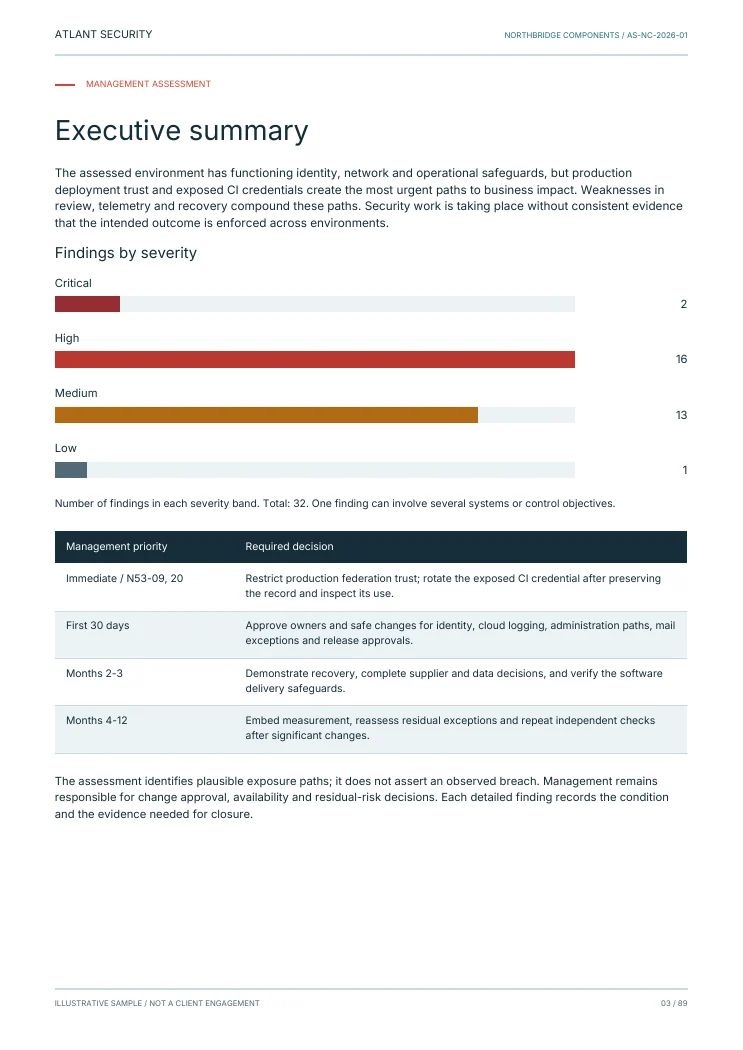
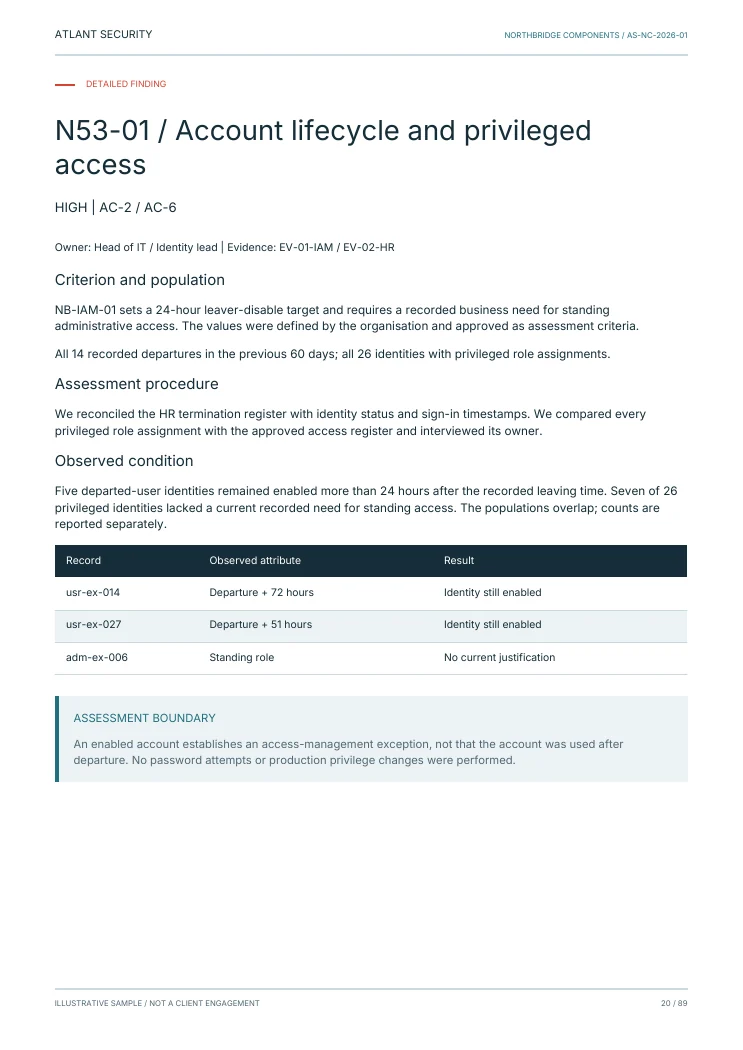
From a management overview to an actionable finding.
WHAT WE REVIEW
An information security assessment can cover these areas. We agree the environment, criteria and depth before the work starts.
Accounts, authentication, administrator privileges and access to sensitive data.
Endpoints, networks, servers and the cloud environments in your scope.
Logging, alerts, incident procedures, backups and recovery evidence.
Policies, ownership, supplier risks and how controls work day to day.
Development practices, secrets, dependencies and delivery pipelines in broader packages.
Controls assessed against your agreed criteria. One framework in Essentials; wider mapping in broader packages.
Framework-led, environment-specific. NIST SP 800-53 can structure the review across 20 control families. Applicable controls and test depth follow your scope.
Certification and exploitation-based testing are separate. Need a Microsoft 365 audit or penetration test?
PACKAGES & PRICING
Three starting points. Your written proposal confirms the coverage, deliverables and fixed price.
Focused audit for startups and small teams.
Full-scope audit for growing companies.
Multi-entity, multi-country audit programs.
| Package | Systems & controls | Evidence you provide | What you receive | Delivery & boundaries |
|---|---|---|---|---|
| Essentials AuditFrom $5,000Up to 50 employees | Selected access, configuration, resilience and information security controls in one agreed cloud or on-premises environment, assessed against one framework. | System inventory, relevant access and configuration exports, policies, backup records and the named people responsible for the selected controls. | Executive summary and a prioritised remediation list for the agreed scope. | Single environment and framework. A 14-day delivery target starts at kickoff when the agreed access and evidence are ready. Detailed technical reporting and cross-environment reviews are not automatically included. |
| Comprehensive AuditFrom $12,000Up to 500 employees | Agreed cloud and on-premises systems; Microsoft 365, Google Workspace and AWS where applicable. Secure software development and DevSecOps practices, with mapping to the agreed frameworks. | Environment and application inventories, scoped read-only access or configuration exports, control evidence, relevant development/pipeline records and interviews with system owners. | Executive and technical reports, prioritised remediation, an Information Security Program Plan, consulting sessions and 30-day follow-up Q&A. | Systems, framework mappings, sampling and test depth are specified in the proposal. Delivery depends on the agreed scope and evidence availability; the Essentials 14-day target does not apply automatically. |
| Enterprise AuditFrom $25,000500+ employees / multiple locations | Agreed multi-entity and hybrid environments, cloud platforms, remote access, secure development and DevSecOps, plus vendor and supply-chain risks. | Entity and system inventories, access and control evidence across agreed locations, supplier records and interviews with business and technical owners. | Executive and technical reporting, a board-ready presentation, full Information Security Program Plan, a dedicated engagement manager and 60-day follow-up support. | Entities, locations, platforms, framework coverage and reporting requirements are agreed explicitly. Your proposal sets milestones, dependencies and delivery dates. |
Entities, environments, system complexity, frameworks, testing depth and reporting needs.
Essentials targets 14 days once access and evidence are ready. Broader engagements have agreed delivery dates.
Review your report before payment under the written terms agreed for your engagement.
HOW IT WORKS
Whether you need an independent risk assessment, board assurance or answers for a customer review, start with the decision you need to make.
Systems, deliverables, fee and delivery date. Confirmed in writing.
Configuration, records, interviews and authorised checks.
Validate observations and connect each finding to its risk and fix.
Walk through your reports, priorities and agreed follow-up.
Both start with your business question. An audit reviews controls against agreed criteria; a posture or risk assessment looks at weaknesses and their business impact. We can combine these with gap analysis in one clearly scoped engagement.
Essentials starts at $5,000: one environment, one framework, an executive summary and remediation priorities. Comprehensive starts at $12,000 and Enterprise at $25,000. Their wider coverage and additional reports are not included in Essentials. We confirm the scope and fixed price before work begins.
Essentials targets 14 days from kickoff, once the agreed access and evidence are ready. Comprehensive and Enterprise timelines depend on scope. Your proposal confirms the delivery date and what we need from your team.
We agree the system inventory, configuration exports, policies, records, interviews and any read-only access needed for the selected checks. Evidence is shared through agreed secure channels. Do not send passwords or sensitive records through the enquiry form.
Yes. We tailor the agreed review and reporting to the decision you need to make — whether that is reducing exposure, answering a board request or getting a stalled customer security review moving. Tell us who needs the findings and why.
No. This is an independent security review. Framework mapping can support readiness but does not issue a certification, accreditation or SOC 2 report. Exploitation-based penetration testing is scoped separately.
You can start by email using the form; a scheduled online meeting is optional. Scope, price, delivery and payment terms are agreed in writing. You review the report before payment under those agreed terms.
NEXT STEP
Start by email, or choose a 30-minute online meeting.