Cybersecurity Companies in San Francisco: The 2026 Buyer’s Guide
Founder and Principal Security Consultant - CISSP, CEH, CHFI, Mandiant
We have probably seen your problem before. Our smallest client had eight employees. Our largest secures the nuclear power plant of the United Arab Emirates. Whatever shape yours is, tell us about it and we will tell you how we would fix it.
Search "cybersecurity companies in San Francisco" and Google returns two completely different kinds of business, mixed together. One is local IT and security firms with a San Francisco address and a phone number that a human answers. The other is global security software vendors that happen to be headquartered in the city. They solve different problems, they are bought by different people, and confusing them is the most expensive mistake in this category.
This guide separates them. Below you will find the firms that actually show up in Google's local results for San Francisco, what each of them is genuinely good at, and the product companies headquartered here that you may be evaluating instead. Every screenshot is the company's live homepage, captured on 14 September 2026.
Who publishes this guide
Atlant Security is a cybersecurity consultancy and appears in the list below. We have placed ourselves where we belong on merit rather than at the top, we describe the firms we compete with accurately, and we say plainly where another firm is the better call. You should still weigh this the way you would weigh any guide written by a participant.
Start Here
Which kind of firm do you actually need?
Before comparing names, work out which of these three sentences describes you. It removes about eighty per cent of the options immediately.
| If this is you | What you need | What to ignore |
|---|---|---|
| "Nobody runs our laptops, email or network. Things break and we improvise." | A managed IT provider with a real security practice. Jones IT, Xantrion, TruAdvantage, Intelligent Technical Solutions, Varsity, Xterra. | Product vendors. You have nobody to operate the product. |
| "A customer or investor is asking for SOC 2, ISO 27001 or a completed security questionnaire, and the deal is stuck." | A security consultancy or compliance specialist. Atlant Security, Vanta, and the assessment practices at NCC Group. | An MSP that treats compliance as a checkbox in its stack. |
| "We have engineers. We need someone to attack what we built and prove it holds." | Offensive security. Bugcrowd, HackerOne, Synack, NCC Group. | Anything sold as an all-in-one platform. |
The honest version
Most San Francisco companies under about 200 staff need the first row and think they need the third. Penetration testing an environment nobody administers produces a long report and no improvement, because there is no one to act on it.
San Francisco Providers
The local field, firm by firm
These are the firms that appear in Google's local results for San Francisco. Listed alphabetically. Ranking a managed IT provider against a compliance consultancy produces a league table that flatters whoever wrote it, so there is no numbered order here. Every quote below is taken from the company's own site, and every screenshot was captured on 14 September 2026.
Atlant Security
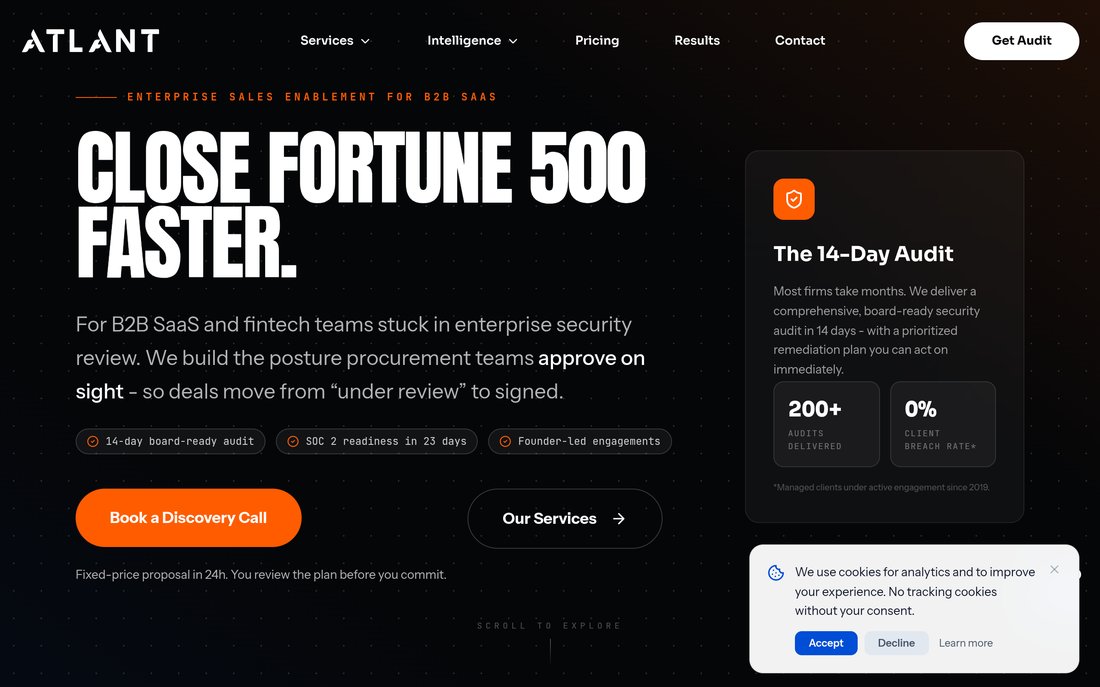
| Type | Security consultancy. Not a managed IT provider. |
| Focus | Companies blocked by a customer security review, a compliance deadline or an insurer |
| Headline services | IT security audit, SOC 2 and ISO 27001 readiness, virtual CISO, penetration testing |
| Model | Fixed price agreed in writing, report delivered before invoice |
| Team | Led personally by Alexander Sverdlov, CISSP, CEH, CHFI, Mandiant |
We audit what you actually run across 20 NIST 800-53 domains, rank findings by what an attacker can reach rather than by scanner severity, then close the gaps with your engineers. Alexander was on the Microsoft security consulting team and has served as an external consultant to the nuclear power plant of the UAE. The consultant who scopes the work is the one who does it.
Strengths
- Fixed price agreed before work starts, no hourly meter
- You read the full report before the invoice arrives
- Vendor neutral: no software resale, no commissions
- Published prices, which is rare in this category
- 14 days from kickoff to a ranked remediation plan
Limits
- We do not run your helpdesk, laptops or network
- A two-person senior team, so capacity is genuinely limited
- No 24/7 monitoring desk; that is an MDR purchase
- If nobody administers your environment, hire an MSP first
Best for: a company whose enterprise deal is stuck behind a security questionnaire. See the IT security audit, SOC 2 readiness and published prices. Go elsewhere if what you need is someone to run your technology day to day. We say that on the scoping call rather than selling you an audit you cannot yet act on.
Intelligent Technical Solutions (ITS)
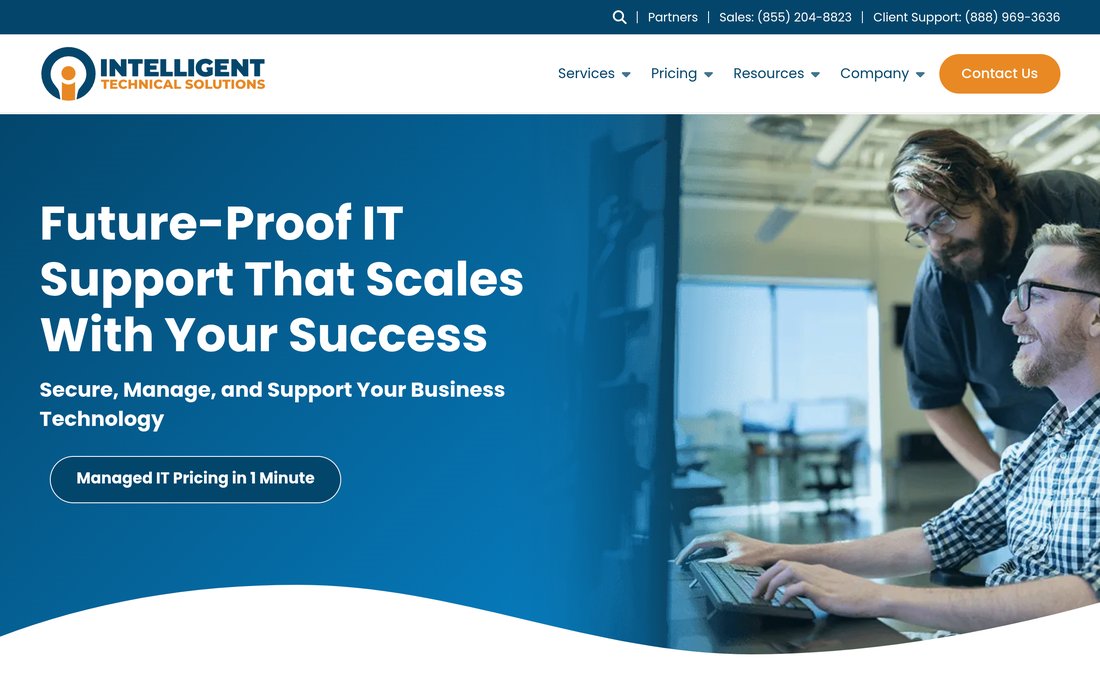
Future-Proof IT Support That Scales With Your Success
| Type | Multi-city managed IT provider |
| Offices | Thirteen, including San Francisco, Oakland, Sacramento, LA, Seattle, Chicago, Dallas |
| Services | Managed IT, cybersecurity, co-managed IT, cloud, compliance, VoIP, healthcare IT, AI as a service |
| Notable | Publishes a managed IT pricing estimator; 24-hour support |
Strengths
- Genuine 24-hour coverage, not an answering service
- A pricing estimator before you speak to sales, which almost nobody offers
- Thirteen offices, so multi-site businesses get one contract
- Co-managed option if you already have an IT person
Limits
- Breadth over depth: the service list runs from VoIP to AI as a service
- Security sits inside a managed contract rather than standing alone
- A national footprint means you are one of many accounts
Best for: a multi-site business that wants one provider for everything and values round-the-clock coverage over specialist security depth.
Jones IT
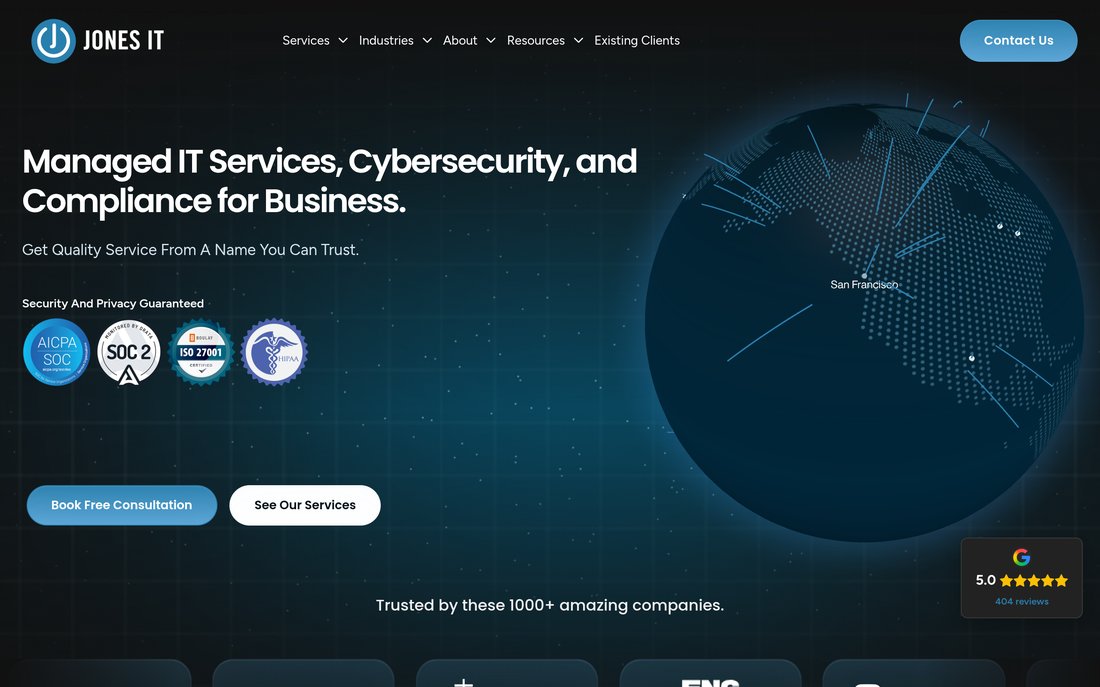
We do not just consult; we partner with you to design, build, and run high-performing infrastructure and processes that keep your business moving forward.
| Type | Managed IT provider with a compliance practice |
| Locations | San Francisco, Oakland, Palo Alto, Silicon Valley |
| Services | Fully managed IT, co-managed IT, cybersecurity and compliance management, short-term projects |
| Notable | A three-month "Compliance Kickstarter"; cites SOC 2 Type 2, ISO 27001 and HIPAA |
Strengths
- By far the largest volume of public reviews of any provider in the local results
- Co-managed model works if you have one internal IT person already
- A time-boxed compliance programme rather than an open-ended retainer
- Genuinely Bay Area: four named offices, all local
Limits
- Compliance is a programme they run, not an independent assessment
- The same firm running your IT cannot objectively audit your IT
- Bundled pricing makes it harder to see what security actually costs
Best for: a growing San Francisco company with no internal IT that wants daily operations, baseline security and a first pass at compliance under one contract.
TruAdvantage
Strategic, Secure, White Glove IT. People First, Tech Second.
| Type | Managed IT and cybersecurity provider |
| Offices | San Jose (HQ, 3031 Tisch Way) and San Francisco (50 California St, Suite 1500) |
| Client size | Stated focus on 20 to 250 employees |
| Sectors | Nonprofits, healthcare, life sciences, finance and accounting, startups |
| Recognition | MSP 501 ranked #1 in the Bay Area, CRN MSP 500, Great Place to Work, SOC 2 Type 2 |
Strengths
- The stated 20 to 250 band is exactly where a first compliance demand lands
- Holds its own SOC 2 Type 2, so it has lived the process it sells
- Two Bay Area offices with published street addresses
- 24/7 live support and a strong public award record
Limits
- Six "managed" product lines is a wide surface for a firm this size
- Compliance support is not the same as an independent readiness assessment
- Headquarters is San Jose, so an SF-first buyer is served from a satellite
Best for: a 20 to 250 person Bay Area company that wants its managed IT provider to carry part of the compliance load rather than engaging a separate consultancy.
Varsity Technologies
Your mission deserves more than generic IT support. At Varsity, we go beyond the limits of traditional MSPs, delivering custom technology strategies designed for nonprofits, foundations, and social impact organizations.
| Type | Managed IT provider with a sector focus |
| Locations | San Francisco, San Jose, Los Angeles, Sacramento, Stockton |
| Sectors | Nonprofits, foundations, social impact, higher education, healthcare |
| Services | Managed IT, cybersecurity, cloud and Azure, training, data protection and governance |
| Compliance | HIPAA, FERPA audits, PCI audits, vulnerability assessment |
Strengths
- A real sector specialism, not a page of vertical keywords
- FERPA experience is genuinely uncommon among Bay Area MSPs
- Training as a service line, which matters where staff turnover is high
- Understands grant cycles and board reporting, which shape nonprofit budgets
Limits
- If you are a venture-funded SaaS company you are not their core client
- Five California offices spread the team thin geographically
- Security is one line among many rather than the centre of the business
Best for: San Francisco nonprofits, foundations and education institutions, where funding cycles and reporting obligations differ from a startup's.
Xantrion
| Type | Managed IT and managed cybersecurity provider |
| Locations | East Bay, San Francisco Bay Area, San Jose, Sacramento, Los Angeles, San Diego |
| Client size | Mid-market, with a stated ratio of three to ten clients per virtual CIO |
| Sectors | Finance, life sciences, legal, manufacturing, healthcare, accounting, government |
| Recognition | Tier 1 Microsoft CSP, AICPA SOC 2 certified, MSP 501 2026 winner, MSSP Alert Top 250 |
Strengths
- Three to ten clients per virtual CIO is a real published constraint on load
- MSSP Alert Top 250 listing means security is an actual practice, not a bolt-on
- Tier 1 Microsoft CSP status matters if you run Microsoft 365 and Azure
- Around twenty-five years in the Bay Area
Limits
- East Bay rooted, so an SF-only buyer may prefer someone across the bridge
- Mid-market focus means a fifteen-person startup is below their line
- The site blocks automated tools, which is a minor signal about how they operate
Best for: established mid-market Bay Area businesses, particularly Microsoft-heavy ones, wanting a long-term managed relationship with a named virtual CIO.
Xterra Solutions
High quality IT managed services at a fraction of the cost of hiring your own team.
| Type | Managed IT provider |
| Location | San Francisco, serving the Bay Area, ten-plus years operating |
| Services | Fully managed and co-managed IT, 24x7 service desk, monitoring, cloud service management, security, IT health checks |
| Sectors | Financial services, education, government, professional services |
Strengths
- San Francisco based rather than serving SF from elsewhere
- 24x7 service desk despite being a smaller firm
- Financial services and government experience brings audit familiarity
- IT health checks give you a low-commitment way to start
Limits
- Smallest of the local providers here, so depth depends on individuals
- Security is one line item, not a standalone practice
- Positioning leads on cost substitution rather than on outcomes
Best for: smaller San Francisco offices, especially in regulated professional services, that want a local provider who will physically turn up.
Comparison
Local providers side by side
The columns that actually differentiate these firms. Reviews are indicative of visibility rather than quality, and none of these firms publishes client outcomes, so treat them as a measure of how established a provider is.
| Firm | What it is | Client size | Security depth | Independent of your IT? | Best fit |
|---|---|---|---|---|---|
| Atlant Security | Consultancy | Roughly 20 to 500 | Core business | Yes | Stalled deal, compliance deadline |
| ITS | National MSP | Any | Inside managed contract | No | Multi-site, wants 24/7 |
| Jones IT | Bay Area MSP | Startup to enterprise | Inside managed contract | No | No internal IT at all |
| TruAdvantage | Bay Area MSP | 20 to 250 | Compliance-leaning | No | First compliance requirement |
| Varsity | Sector MSP | Mid-sized | Inside managed contract | No | Nonprofit, foundation, education |
| Xantrion | MSP and MSSP | Mid-market | Named practice | No | Microsoft-heavy mid-market |
| Xterra | SF MSP | Small to mid | Inside managed contract | No | Small SF office, on-site needs |
The column most buyers skip
Independence. If the firm that configured your environment also assesses it, the assessment has a conflict baked in, and some auditors will say so. That is not a reason to avoid MSPs, it is a reason to keep the assessment separate from the operations. Plenty of San Francisco companies run exactly that split: one firm operates, another checks.
The Product Tier
Security companies headquartered in San Francisco
These companies are headquartered in San Francisco and they are why the city dominates security industry coverage. Almost none of them will sit with a fifty-person company and fix its Microsoft 365 tenant. They sell products, usually to buyers who already have a security team.
Cloudflare
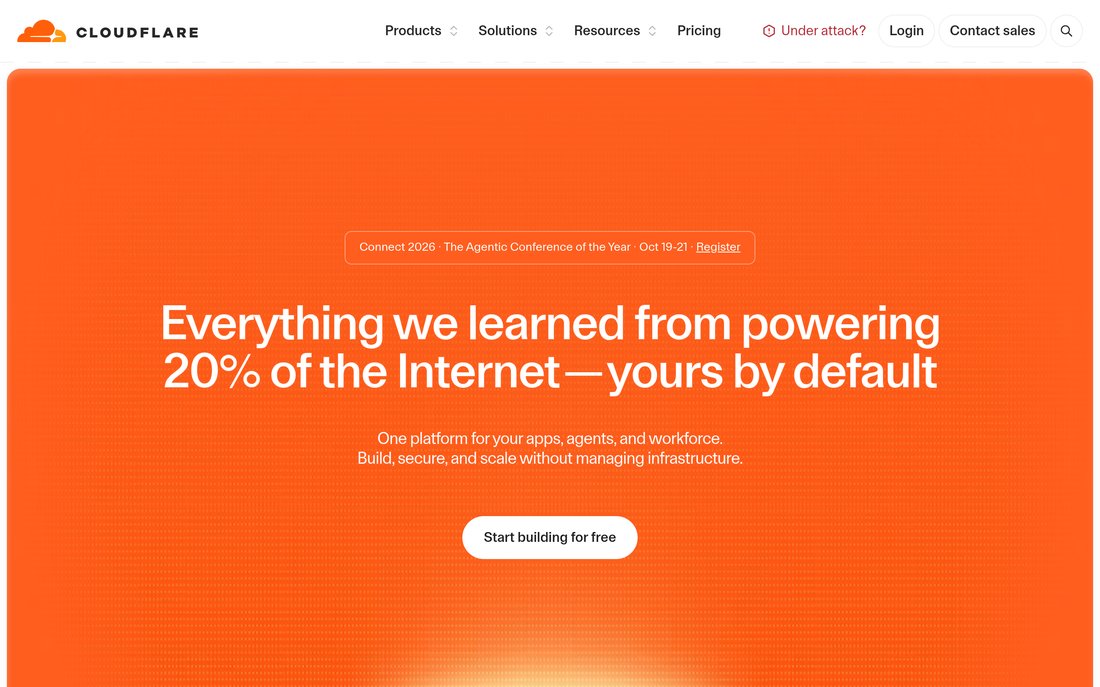
Network and application security delivered at the edge: DDoS protection, web application firewall, zero trust network access and DNS. Genuinely San Francisco headquartered. Self-serve tiers make it one of the few names here a small company can actually adopt without a sales process.
Okta
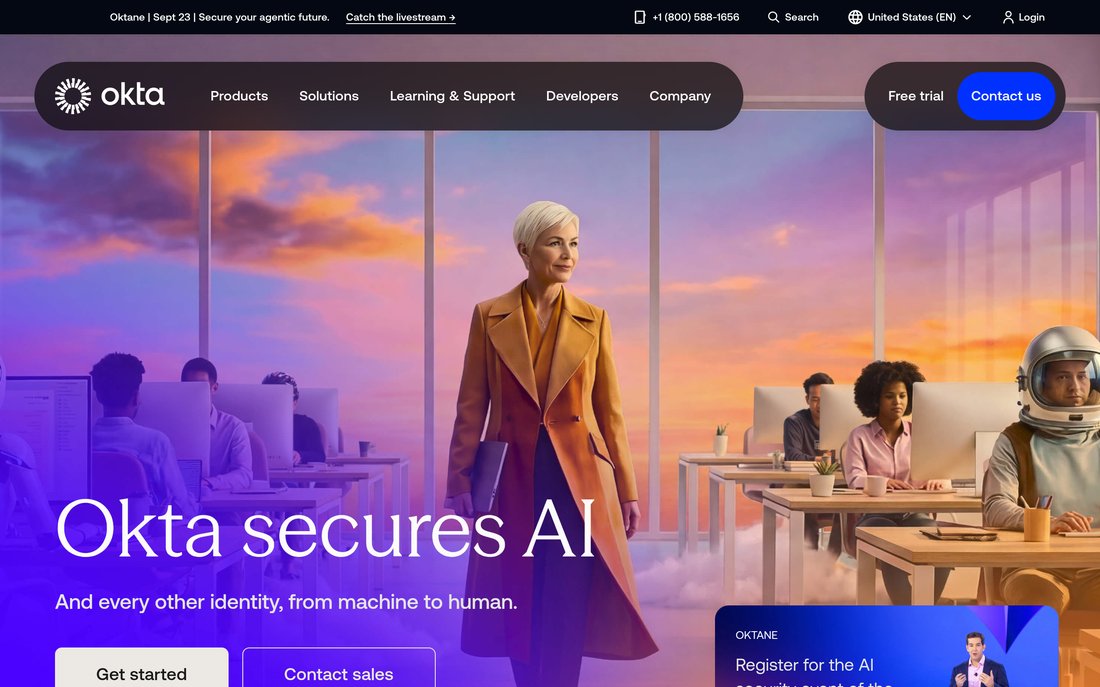
Identity is the control that matters most and the one most often left half-configured. Okta sells workforce and customer identity, single sign-on and lifecycle management. Buying it is the easy part; configuring it so that leavers actually lose access is the part people underestimate.
Bugcrowd
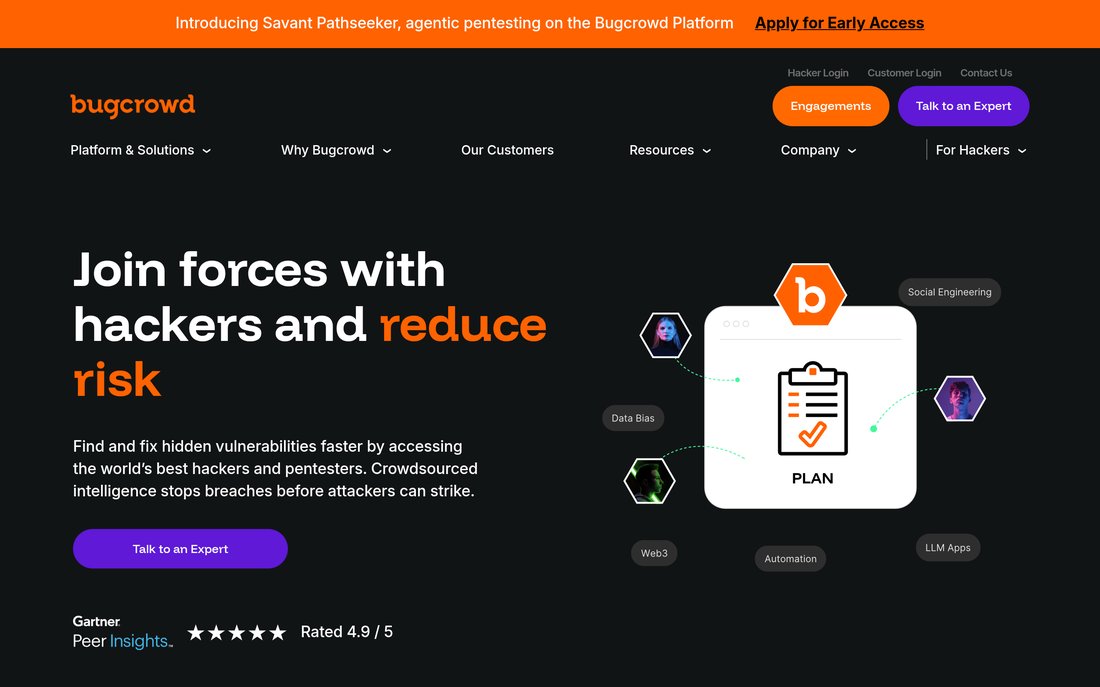
Crowdsourced penetration testing, bug bounty programmes, red teaming and vulnerability disclosure, run across a researcher community. Useful once you have a product worth attacking and the engineering capacity to fix what comes back.
HackerOne
The other major crowdsourced testing platform, covering bug bounty, pentest delivery, code review and adversarial testing of AI systems. The choice between HackerOne and Bugcrowd usually comes down to programme management style rather than researcher quality.
Abnormal
Email remains the most common way in, and Abnormal models normal communication behaviour to catch account takeover and business email compromise that signature-based filters miss. Layers on top of Microsoft 365 or Google Workspace rather than replacing them.
Coalition
Cyber insurance bundled with security tooling and incident response. Increasingly relevant because insurers now set the security bar: multi-factor authentication, tested backups and endpoint detection are becoming conditions of cover rather than discounts.
Vanta
Automates evidence collection and control monitoring for SOC 2, ISO 27001 and a long list of other frameworks. Worth being precise about what it does: it collects and monitors evidence. It does not fix a broken control, and no platform issues the report. An accredited auditor does that.
NCC Group
Not headquartered here, but its San Francisco office has deep roots in the local testing scene. Security assurance, penetration testing and specialist hardware and cryptography review at a depth few firms match.
Synack
Bay Area rather than San Francisco proper. Continuous penetration testing through a vetted researcher network, aimed at organisations that need testing to be ongoing rather than annual.
Comparison
The product tier side by side
What each one actually replaces, who operates it after purchase, and whether a company under a hundred people can realistically adopt it without a dedicated security hire.
| Company | Category | Replaces | Who operates it | Viable under 100 staff? |
|---|---|---|---|---|
| Cloudflare | Edge and network security | WAF appliance, DDoS scrubbing, VPN | Your engineers | Yes, self-serve tiers |
| Okta | Identity and access | Scattered per-app logins and manual offboarding | IT or ops | Yes, but configuration is the work |
| Bugcrowd | Crowdsourced testing | An annual pentest engagement | Someone must triage findings | Only with engineers to fix |
| HackerOne | Crowdsourced testing | An annual pentest engagement | Someone must triage findings | Only with engineers to fix |
| Abnormal | Email security | Secure email gateway | Runs largely on its own | Yes |
| Coalition | Cyber insurance plus monitoring | A standalone insurance policy | The insurer, plus your controls | Yes |
| Vanta | Compliance automation | Spreadsheets of evidence | You, plus whoever fixes the gaps | Yes, with a consultancy alongside |
| NCC Group | Security assurance | In-house testing capability | Delivered as a service | Expensive at that size |
| Synack | Continuous pentesting | Point-in-time testing | Delivered as a service | Usually above that size |
The trap in this table
Four of these are bought by companies that then have nobody to operate them. A bug bounty programme with no engineer to fix what comes back becomes a list of things you now demonstrably knew about. That is a worse legal position than not having looked. Buy testing when you have the capacity to act on it.
Budget
What it costs, roughly
Nobody in this market publishes everything, but the shape of the spend is predictable. Ranges below are typical Bay Area figures for a company of 20 to 200 staff.
| Engagement | Typical model | Rough Bay Area range | What moves the number |
|---|---|---|---|
| Managed IT with security included | Per user, per month | $150 to $250 per user | Headcount, devices, whether 24/7 is included |
| IT security audit | Fixed price project | From $5,000 up to 50 staff | Number of environments and frameworks in scope |
| SOC 2 readiness | Fixed price project | From $3,000 | How much already exists |
| SOC 2 Type II audit itself | Fixed fee to a CPA firm | $15,000 to $50,000 | Trust criteria in scope, auditor, observation window |
| Compliance automation platform | Annual subscription | $8,000 to $25,000 a year | Frameworks, headcount, integrations |
| Penetration test | Fixed price per scope | $8,000 to $40,000 | Application count, whether it is manual or scanner-led |
| Virtual CISO | Monthly retainer | From $3,300 a month | Days per month, board reporting, incident cover |
Where budgets get destroyed
Buying the compliance platform first. It collects evidence of controls you have not built yet, so you pay for a subscription for months before it can show anything useful, then discover the gaps a fortnight before audit fieldwork. Fix first, automate the evidence second.
Local Context
What San Francisco actually changes about the decision
Three things make the San Francisco buying decision different from the same purchase in most other US cities.
The trigger is commercial, not technical
In this city security spending is usually unlocked by a customer, an investor or an insurer rather than by an incident. An enterprise prospect sends a vendor security questionnaire, or a term sheet arrives with diligence attached, and suddenly the work has a deadline. That means the right provider is the one who can produce defensible evidence on that deadline, not the one with the longest capability list.
CCPA and CPRA apply earlier than people expect
California privacy law reaches businesses well below the size at which they think of themselves as regulated, and it carries a statutory duty to maintain reasonable security procedures. Reasonable is decided after the fact, by reference to what you documented and did. That makes written evidence of your decisions worth more here than in states without an equivalent statute.
Cloud-native means the perimeter is identity
The typical San Francisco company has no server room. Everything is in AWS, Google Cloud or Azure, with Microsoft 365 or Google Workspace on top and a long tail of SaaS nobody has inventoried. A provider whose security practice is built around firewalls and antivirus is solving the previous decade's problem. Ask specifically how they secure identity, cloud configuration and SaaS access.
One question that sorts providers quickly
Ask: "When you finish, what do I have that I can send to a customer who asks whether we are secure?" A provider selling operations will describe tools they installed. A provider selling outcomes will describe a document you can forward. Both are legitimate. You need to know which one you are buying.
Process
How to run the selection without wasting a quarter
- Write down the trigger first. One sentence: the customer asking, the framework named, the date. Every proposal should answer that sentence. Ones that do not are selling you something else.
- Ask who does the work. Not who attends the pitch. In this market the gap between the person selling and the person delivering is the single largest source of disappointment.
- Get the price in writing before the work starts, with what changes it. Hourly billing on an open scope is how a two-week engagement becomes a quarter.
- Ask for a redacted deliverable. Any firm that has done this before can show you a sanitised report. If they cannot, you are their pilot.
- Check they will sit with your engineers. A finding handed over without a fix is work transferred to you at consultancy prices.
- Confirm who signs. For SOC 2 and ISO 27001 the certificate comes from an accredited auditor or CPA firm, never from the consultancy or the platform preparing you. Any implication otherwise should end the conversation.
FAQ
Frequently asked questions
Who are the top cybersecurity companies in San Francisco?
It depends which of two industries you mean. For local service providers, the firms that consistently appear in San Francisco results are Jones IT, Xantrion, TruAdvantage, Intelligent Technical Solutions, Varsity Technologies, Xterra Solutions and Atlant Security. For security products headquartered in the city, the major names are Cloudflare, Okta, Bugcrowd, HackerOne, Abnormal, Coalition and Vanta. The first group works with you. The second sells you software.
How much does a cybersecurity company in San Francisco cost?
Managed IT with security included typically runs on a per-user monthly fee, and Bay Area rates sit at the upper end of the US range. Project work is different: a SOC 2 readiness assessment starts around $3,000, a full IT security audit around $5,000 for companies up to fifty staff, and a virtual CISO retainer around $3,300 a month. Any firm that will not give you a number before a scoping call is planning to price you rather than the work.
Do I need a San Francisco company, or can the work be done remotely?
Almost all of it can be done remotely, and most of it now is. Physical presence matters for three things: hardware, office network installation, and the confidence some boards take from being able to meet the person. If none of those apply, widen the search and choose on competence rather than postcode.
What is the difference between a managed IT provider and a security consultancy?
A managed IT provider runs your technology day to day and is accountable for it working. A security consultancy assesses how exposed you are, tells you what to fix and helps you fix it, then leaves. Most San Francisco companies under 200 staff need the first. Companies with a compliance deadline or a stalled enterprise deal need the second. A number need both, in that order.
We need SOC 2 because a customer is asking. Who do we call?
A compliance automation platform such as Vanta will collect and monitor evidence. A consultancy will close the gaps that stop you passing. An accredited CPA firm issues the report, and it cannot be the same firm that prepared you. Budget for all three roles; the common failure is buying the platform, assuming it is the whole job, and discovering the gaps a fortnight before fieldwork.
Does CCPA apply to a small San Francisco startup?
It applies well below the size most founders assume, and it carries a duty to maintain reasonable security procedures appropriate to the personal information you hold. Reasonable is judged after an incident, against what you documented and did beforehand. That is why written decisions matter more in California than in states without an equivalent statute.
How long does a security engagement take?
A focused IT security audit runs about fourteen days from kickoff to a ranked remediation plan. SOC 2 readiness is typically four to eight weeks depending on how much exists already. A Type II report then requires an observation window of three to twelve months, which is the part that cannot be compressed and the part most often discovered too late.
What should I ask a San Francisco security firm on the first call?
Four questions. Who will actually do the work. What the fixed price is and what changes it. What document I hold at the end that I can send to a customer. And what you will not do, so I know where the edges are. The answers separate firms faster than any capability matrix.
Next Step
Where to start
If a customer is asking whether you are secure and you cannot answer with a document, that is the problem to solve first, and it is solvable in about two weeks. Our IT security audit covers twenty domains across your live environment and ends with a ranked plan; you read the report before you pay. If the requirement is specifically SOC 2, start with SOC 2 readiness. If you need a named security leader for the board without a $280,000 hire, that is the virtual CISO engagement. Prices for all of them are published.
And if what you actually need is somebody to run your laptops and network day to day, hire one of the managed providers above. We will tell you that on the call rather than sell you an audit you are not ready to use.
Looking wider than this list? cybersecuritycompanies.io is a free directory of cybersecurity companies worldwide, filterable by category, location and credentials.
Want to know where you actually stand?
A fixed-price IT security audit answers that in 14 days: 20 NIST 800-53 domains checked against your live environment, findings ranked by what an attacker can reach, and a remediation plan with named owners. You read the report before you pay.
See what the 14-day audit covers
Alexander Sverdlov
Founder of Atlant Security. CISSP, CEH, CHFI and Mandiant certified. Author of 2 information security books, cybersecurity speaker at the largest cybersecurity conferences in Asia and a United Nations conference panelist. Former Microsoft security consulting team member, external cybersecurity consultant at the Emirates Nuclear Energy Corporation.
Connect on LinkedIn