A Virtual CISO Company That Owns Your Security Programme From $3,300 a Month.
A boutique vCISO firm, not a marketplace: one named virtual CISO, accountable for the outcome
Atlant Security's Virtual CISO (vCISO) service gives your company a seasoned Chief Information Security Officer - on demand, at up to 60% less than a full-time hire. Get SOC 2, ISO 27001, HIPAA, or PCI DSS ready in 90 days or less, backed by our Double-Edge Guarantee.
- Audit-Pass Guarantee - we pay for re-audits if you follow our roadmap
- 30-Day Opt-Out - walk away in month one and keep all deliverables
- 200+ companies protected: Banking, Healthcare, SaaS & Manufacturing
The seat exists whether or not you have filled it. A vCISO is that seat, held by a named person, without the salary.
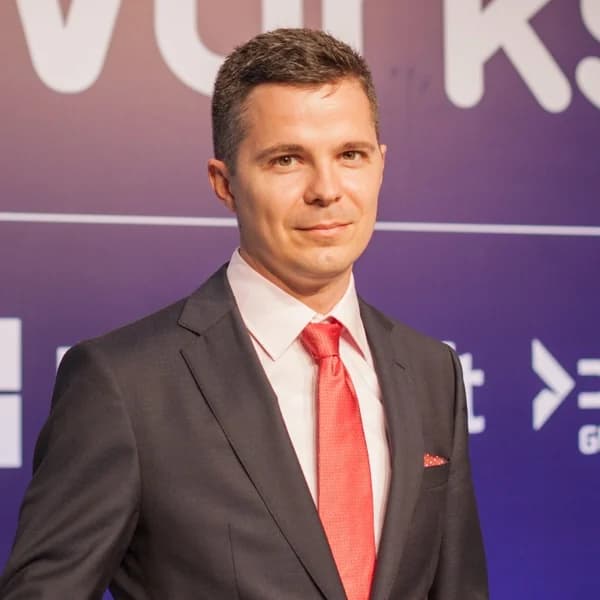
Every Virtual CISO Engagement Is Led by Alexander Sverdlov
Former Microsoft Security Consulting team member. CISSP, CEH, CHFI and Mandiant certified. Secured nuclear energy infrastructure at Emirates Nuclear Energy Corporation. Alexander has personally led 200+ security assessments across 14 countries since 2013. At Atlant Security, the senior consultant who scopes your security program is the same person who builds it, reports to your board, and leads incident response - never handed to junior staff.
Connect on LinkedInvCISO vs. Full-Time CISO: Which Is Right for You?
Most growing companies get significantly more value from a vCISO. Here is the honest comparison.
| Criteria | Virtual CISO (vCISO) | Full-Time CISO |
|---|---|---|
| Annual Cost | From $3,300/mo ($39,600/yr) | $250,000-$400,000+/yr salary alone |
| Time to Start | Days, not months | 3-6 months average time-to-hire |
| Experience Breadth | Cross-industry from 200+ engagements in 14 countries | Single company environment |
| Team Access | Full team of specialists included | Single point of knowledge - no backup |
| Scalability | Scales with your business needs | Fixed headcount regardless of workload |
| Additional Costs | No benefits, bonuses, or equity | Benefits, bonuses, equity on top |
| Compliance Expertise | Deep cross-industry compliance experience | May lack niche compliance expertise |
| Vendor Bias | 100% vendor-agnostic - zero kickbacks | May favor familiar vendor relationships |
| Cancellation | 30-day opt-out with all deliverables kept | Long-term employment contract required |
What Our vCISO Service Includes
A fully managed information security programme covering every layer of your business.
Security Program Ownership
We build, manage, and continuously improve your security program as an embedded member of your leadership team. Not advisory-only - full ownership and accountability.
Compliance Readiness
SOC 2 Type I & II, ISO 27001, HIPAA Security Rule, PCI DSS, NIST 800-171, CMMC, HITRUST, and GDPR. Map controls once, satisfy all applicable standards simultaneously.
Cloud & Infrastructure Security
Microsoft 365 hardening (280+ settings), Google Workspace lockdown, AWS/Azure/GCP configuration review, endpoint protection, and Zero Trust architecture.
Employee Security Awareness
Monthly phishing simulations, security training sessions, and building a security-first culture across your organization.
Board & Executive Reporting
Quarterly board-ready reports covering risk posture, program maturity, compliance status, and strategic recommendations. Designed for non-technical leadership.
Vendor Risk & Incident Response
Third-party security assessments, vendor questionnaire management, supply chain risk oversight. Plus IR planning, tabletop exercises, and breach coordination.
Who Needs vCISO Services?
Our virtual CISO services are built for organizations with real security and compliance obligations - but not yet the budget for a full-time executive hire.
Why B2B Companies Choose Atlant Security as Their vCISO Partner
One named person, reachable, accountable for the outcome rather than the hours.
Compliance Frameworks We Cover
Audit-ready in 90 days or less. Our virtual CISOs have guided companies through every major framework and every client who completed the roadmap has passed their audit to date.
What You Get
Virtual CISO Pricing
A full-time CISO costs $280,000+/year. Our virtual CISO packages deliver the same strategic leadership at a fraction of the cost - with fixed pricing you know before we start.
The same engagement is sold elsewhere as a fractional CISO, a part-time CISO or CISO as a service. The names differ; the question that matters is how many days a month you get and who is accountable to your board.
SMB
For small businesses up to 50 employees.
- Microsoft 365 / Google Workspace security hardening
- Email & communication channel protection
- Endpoint security policy & enforcement
- Website security review & policy creation
- Password management & MFA rollout
- NIST / SOC 2 / CMMC compliance guidance
- Monthly security posture reporting
- Security policy & procedure documentation
Mid-Market
For companies with 50-500 employees.
- Everything in SMB
- Security awareness training for all employees
- Advanced threat protection & monitoring
- Incident response planning & tabletop exercises
- Vendor & third-party risk management
- Multi-framework compliance (SOC 2, ISO, HIPAA, CMMC)
- Board-ready executive reporting
- Audit preparation & auditor liaison
Enterprise
For complex, multi-entity organizations.
- Everything in Mid-Market
- Multi-entity / multi-country security coverage
- Custom security architecture & zero trust design
- M&A cybersecurity due diligence support
- Dedicated security program manager
- Regulatory liaison & compliance reporting
- 24/7 incident response coordination
- Full security team augmentation & hiring guidance
Need a Named NIS 2 Security Officer? Same Seat, Statutory Duties
NIS 2 and the Bulgarian Cybersecurity Act, in force since 13 February 2026, expect essential and important entities to have a named person or unit responsible for network and information security, to own the Article 21 measures, to file the 24-hour early warning and 72-hour incident notification, and to put the management body through cybersecurity training every two years. Board members are personally liable, with fines of EUR 500 to 5,000 each at the full rate since 1 June 2026.
The virtual CISO seat can be appointed as that officer. Nothing about the work changes except that the duties are written into the appointment, the reporting line to management is formal, and the authority has a name to write to. The seat cannot be combined with an independent NIS 2 audit of the same entity, and we say so in the appointment letter.
Municipalities, agencies and other administrative bodies are covered as essential entities. Their heads carry the personal liability even though the bodies themselves are exempt from entity fines. See NIS 2 compliance for the implementation side.
Statutory duties of the seat
- Named officer or unit responsible for network and information security
- Owns the Article 21 measures and their effectiveness review
- Owns the 24-hour early warning and the 72-hour incident notification
- Formal reporting line to the management body, in writing
Management body training every two years
Required by NIS 2 Article 20(2) and the Bulgarian Cybersecurity Act.
- Personal fines of EUR 500 to 5,000 per member, at the full rate since 1 June 2026
- Two-hour session for the board, delivered in English or Bulgarian
- Attendance record and evidence pack retained for the authority
- Repeated on a two-year cycle, by law
NIS 2 Security Officer Seat
A named officer for one essential or important entity, appointed and on record. 12-month term, quarterly exit.
- Appointment letter with duties, reporting line and independence statement
- Ownership of the Article 21 measures and the annual effectiveness review
- Incident classification, 24-hour early warning and 72-hour notification
- Correspondence with the competent authority and the sectoral CSIRT
- Quarterly written report to the management body
- Upgrade to the full vCISO seat at any time, difference only
Management Body Cyber Training
The training NIS 2 Article 20(2) requires of every board member, delivered in English or Bulgarian, repeated every two years.
- Two-hour session for up to twelve board members, on site or remote
- What the law now makes each member personally responsible for
- How to read a risk register, an incident report and an audit finding
- A tabletop walk-through of a reportable incident
- Attendance record and evidence pack for the authority
- Reminder scheduled for the two-year repeat
One-Time Security Packages
Designed for businesses that prefer no monthly fees - just rapid, one-time security sprints. Buy a fixed block of senior security time and pay once. No subscription, no lock-in, just a clear scope and a one-time fee.
10-Hour Package
A focused audit plus hands-on fixes for the highest-impact gaps.
- Focused security audit of your environment
- Prioritized findings with a clear remediation plan
- Hands-on implementation of the highest-impact fixes
- One-time fee, no retainer or subscription
20-Hour Package
Usually enough to secure a business from all angles, in one engagement.
- Everything in the 10-Hour Package
- Usually enough to secure a business from all angles
- Deeper implementation across identity, endpoints, email, and cloud
- One-time fee, no retainer or subscription
How Our Virtual CISO Service Works
Three proven phases. Measurable results from day one.
Maturity Assessment
We conduct a deep-dive review of your current security posture and identify critical gaps.
Program Development
We build a customized security roadmap and prioritize initiatives based on your business risk.
Implementation
We work alongside your team to implement controls, policies, and technical safeguards.
Continuous Improvement
We provide ongoing oversight, board reporting, and prepare you for successful audits.
What phase three actually looks like
A board that receives the same pack every quarter, in the same shape, with last quarter's numbers next to this quarter's. No fire drills before the meeting, no one asking what a finding means, and a record that satisfies an auditor or an insurer without anyone reconstructing it afterwards.
What Our Clients Say
“Atlant Security exceeded our expectations in the process of the assessment and in the report we received. As a Virtual CISO, Alexander displayed the organization, confidence, and professionalism necessary to fulfill this leadership role.”
Nedyalka Yolovska
Managing Director, Pegb Technology FZE
“Under your expert supervision, we have made remarkable progress in fortifying the security posture of our organization. The Security Awareness Training Sessions have proven invaluable in equipping our workforce with the necessary knowledge.”
Syed Haris Ahmed
Manager IT Infrastructure & Security, Qordata
For small projects and ad-hoc work outside our pre-agreed packages or retainers, our standard hourly rate is $460.
Frequently Asked Questions About vCISO Services
Can the virtual CISO also be our named NIS 2 security officer?
What is a Virtual CISO (vCISO)?
How much does a Virtual CISO cost?
How quickly can a vCISO get us compliant?
Is Atlant Security vendor-agnostic?
How much does a full-time CISO cost?
What is the smallest company you've worked with?
Can I cancel at any time?
Do you sell security software?
What does a typical vCISO engagement look like?
Can a vCISO help with investor due diligence?
Do you provide board-level reporting?
What is the difference between a vCISO and a security consultant?
How does pricing work for vCISO services?
What frameworks can a vCISO help us comply with?
Can your vCISO work alongside our existing IT team?
Do you handle incident response?
Get Enterprise-Grade Security Leadership Today
Get Your Roadmap. Tell us about your company, your compliance requirements, and your security concerns. We will tell you exactly what you need, what it costs, and how fast we can get you there. No obligation, no pressure.
Virtual CISO engagements we have actually run
Named clients, in their own words where they agreed to be quoted. Every one of these is a real engagement led personally by Alexander Sverdlov.
Management Financial Group
Long-term client relationship providing enterprise-scale security consulting.
Pegb Technology FZE
Complete security culture transformation - infrastructure security, security awareness, and secure software development.
“Atlant Security exceeded our expectations in the assessment and report. The whole team enjoyed working with Alexander towards achieving our security goals. We highly recommend their services to anyone who is serious about achieving their cybersecurity goals.”
Qordata
Comprehensive security posture improvement across End User Security, Cloud Security, with ongoing Security Awareness Training.
“Under your supervision we are making great progress & the most eye-catching part is that we are developing a secure culture which is helping each and every individual with respect to their personal and professional life.”
Edge
Meaningful impact on security maturity with clear, actionable strategies tailored to operational environment.
“Atlant Security took a methodical and business-aware approach to identifying vulnerabilities, streamlining our compliance efforts, and aligning our security posture with ISO 27001, SOC 2, and HIPAA. Their professionalism, responsiveness, and strategic insight made a meaningful impact on our organization’s security maturity.”
More at success stories, including references clients agreed to share.
Get Your Fixed Price
Related: Compare 15 virtual CISO companies - IT Security Audit - SOC 2 Readiness - Success Stories - Contact Us